Auditing GitHub-to-PyPI Publishing Paths After the LiteLLM Supply-Chain Attack
pr0h0•
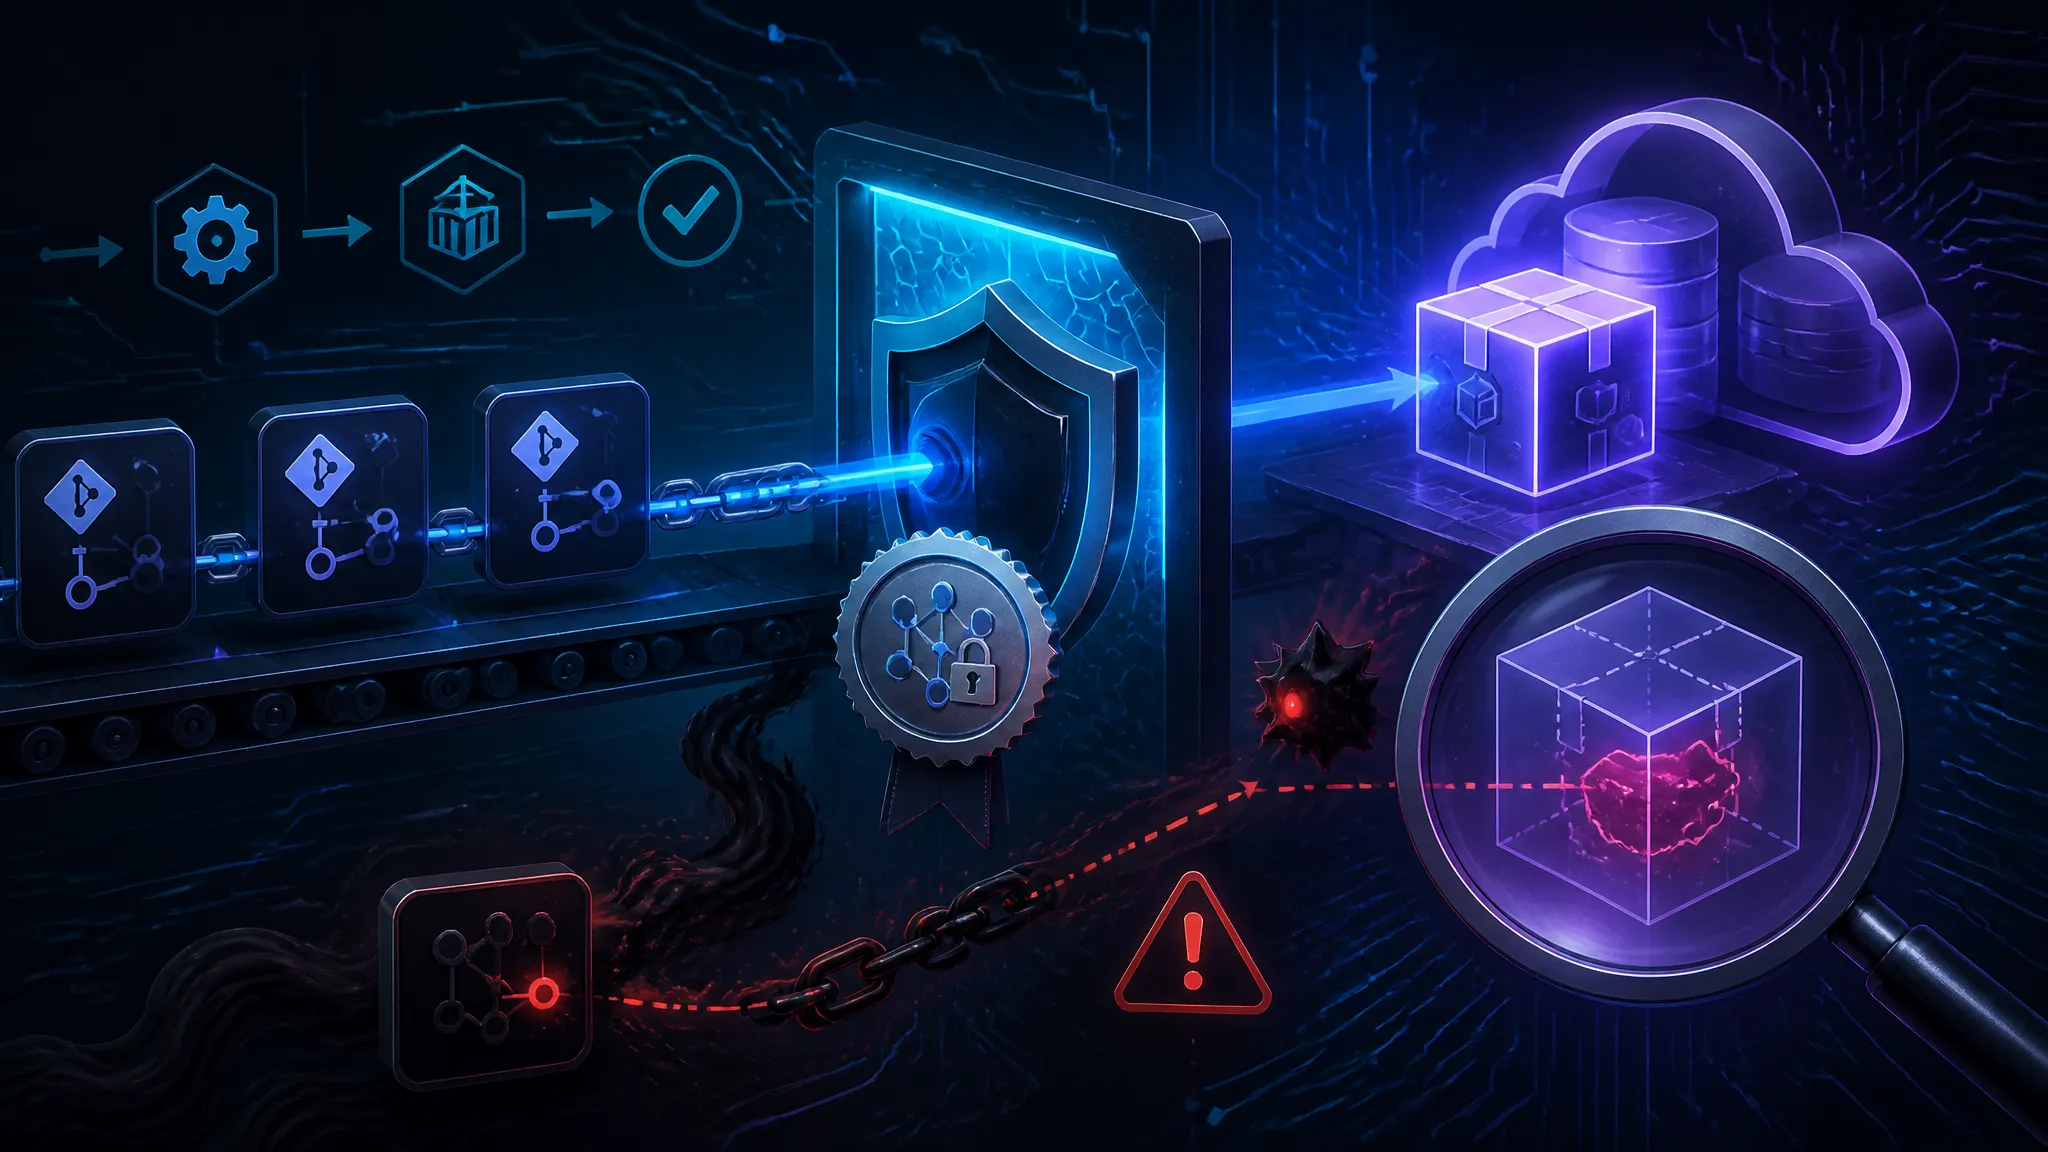
A hands-on audit of GitHub-to-PyPI publishing paths, tracing how LiteLLM's long-exposed GitHub master key enabled a package compromise and what controls — secret scanning, token revocation, trusted publishing, pinning, and attestations — actually close the gap.
supply-chain-securitypypigithub-actions