From a senior to future senior Hackers

2.4T Parameters, 60% Cheaper Per Task: Auditing Qwen4-Max After Retries
Featured

2.4T Parameters, 60% Cheaper Per Task: Auditing Qwen4-Max After Retries

An audit of Qwen4-Max's 2.4T-parameter MoE and its claimed 60% per-task cost cut, using a retry-adjusted cost-per-successful-task worksheet to test whether the vendor's economics survive eval-driven model routing.

pr0h0•
llm-economicsmoeqwenmodel-routinginference-cost
Latest Posts

View all posts →

Latest Videos

View all videos →
Chrome 157.0.8103.50: What CVE-2026-125350 Patched and How to Confirm It's Running

Chrome 157.0.8103.50: What CVE-2026-125350 Patched and How to Confirm It's Running

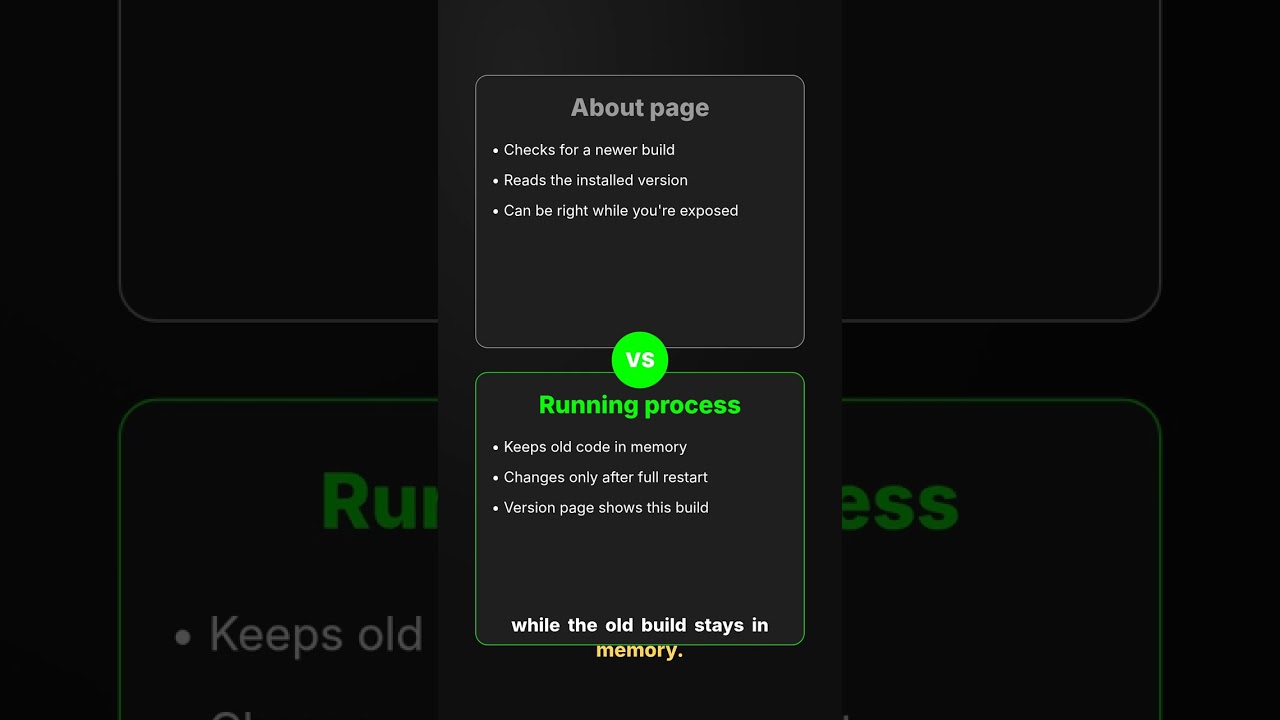
Chrome 157.0.8103.50 carries the fix for CVE-2026-125350, a flaw that reporting says was being exploited before that build shipped. This short covers the part that actually decides your exposure: whether the fixed build is the one executing. What the public record establishes: the CVE is tracked as CVE-2026-125350, the fixed version is 157.0.8103.50, and a CERT-In warning described the flaw as actively exploited. The vulnerability class, the affected component and the full vulnerable range are not stated in the available sources — this video does not guess at them, because a wrong bug-class assumption leads to the wrong interim mitigation and the wrong detections. What the video shows: - Why "Chrome is up to date" is a statement about the update check, not about the process in front of you - How the updater stages new bits on disk while the running process keeps the old code in memory - Reading the running build from Chrome's internal version page, plus the executable path that reveals which install answered - Per-platform checks for the installed build: Google Update's registry key on Windows, bundle metadata on macOS - The exposure gap between an installed version and a running version, and why per-user and side-by-side installs break your asset count All content is defensive and lab-scoped: no exploit code, no target, no credentials. The commands shown only read version information from a machine you administer. Full write-up with the per-platform commands and output: https://hackyjs.com/posts/what-the-chrome-1570810350-update-fixes-in-cve-2026-125350-and-how-to-confirm-it-is-applied

chromezero-daycve-2026-125350
Auditing MCP Servers and Clients for Hidden Session State Before 2026-07-28

Auditing MCP Servers and Clients for Hidden Session State Before 2026-07-28

A short audit of the implicit session state in MCP servers and clients: the initialize handshake, Mcp-Session-Id, SSE replay buffers, server-initiated requests, and the caches and sticky routing teams add themselves. The HackyJS post labels what is confirmed from the 2026-07-28 commentary, what is inferred, and points to the normative text before migration planning. Full write-up: https://hackyjs.com/posts/auditing-your-mcp-server-and-client-for-hidden-session-state-before-the-2026-07-28-stateless-revision

mcpstateless-protocolssession-management
Auditing AI Agent Token Spend: Context, Tool Output, Retries, and Routing

Auditing AI Agent Token Spend: Context, Tool Output, Retries, and Routing

Cost per call hides where agent tokens actually go. This short traces the audit across repeated context, tool output, retries, and routing, then shows the span model and ledger row that make cost per successful task measurable. Read the full playbook with instrumentation code and a worked trace: https://hackyjs.com/posts/auditing-ai-agent-token-spend-context-tool-output-retries-and-routing

ai-agentstoken-optimizationllm-cost