Migrating a Scheduling Feature from Date to Temporal: DST, Durations, and Month Math
A practical guide to migrating a scheduling feature from JavaScript Date to Temporal, covering DST handling, duration arithmetic, and month-based calculations.

A practical guide to migrating a scheduling feature from JavaScript Date to Temporal, covering DST handling, duration arithmetic, and month-based calculations.

Build a JavaScript red-team harness that adversarially tests coding agents for monitor tampering, privilege escalation, and evasion before deployment.

As Microsoft, Nvidia, and AgentR push AI agents into operating systems and browsers, JavaScript developers should expose structured, semantic interfaces that agents can call directly instead of relying on fragile LLM-driven DOM automation.

A code-level analysis of the React Server Components denial-of-service vector that lets a single crafted request exhaust Next.js App Router server resources, along with the defensive configurations and mitigations developers should apply.

A hands-on test of whether Amazon's 2B Strands Decider can reliably gate JavaScript agent tool calls when stacked against explicit prompt-based rules, and where the lightweight decision layer wins or breaks.

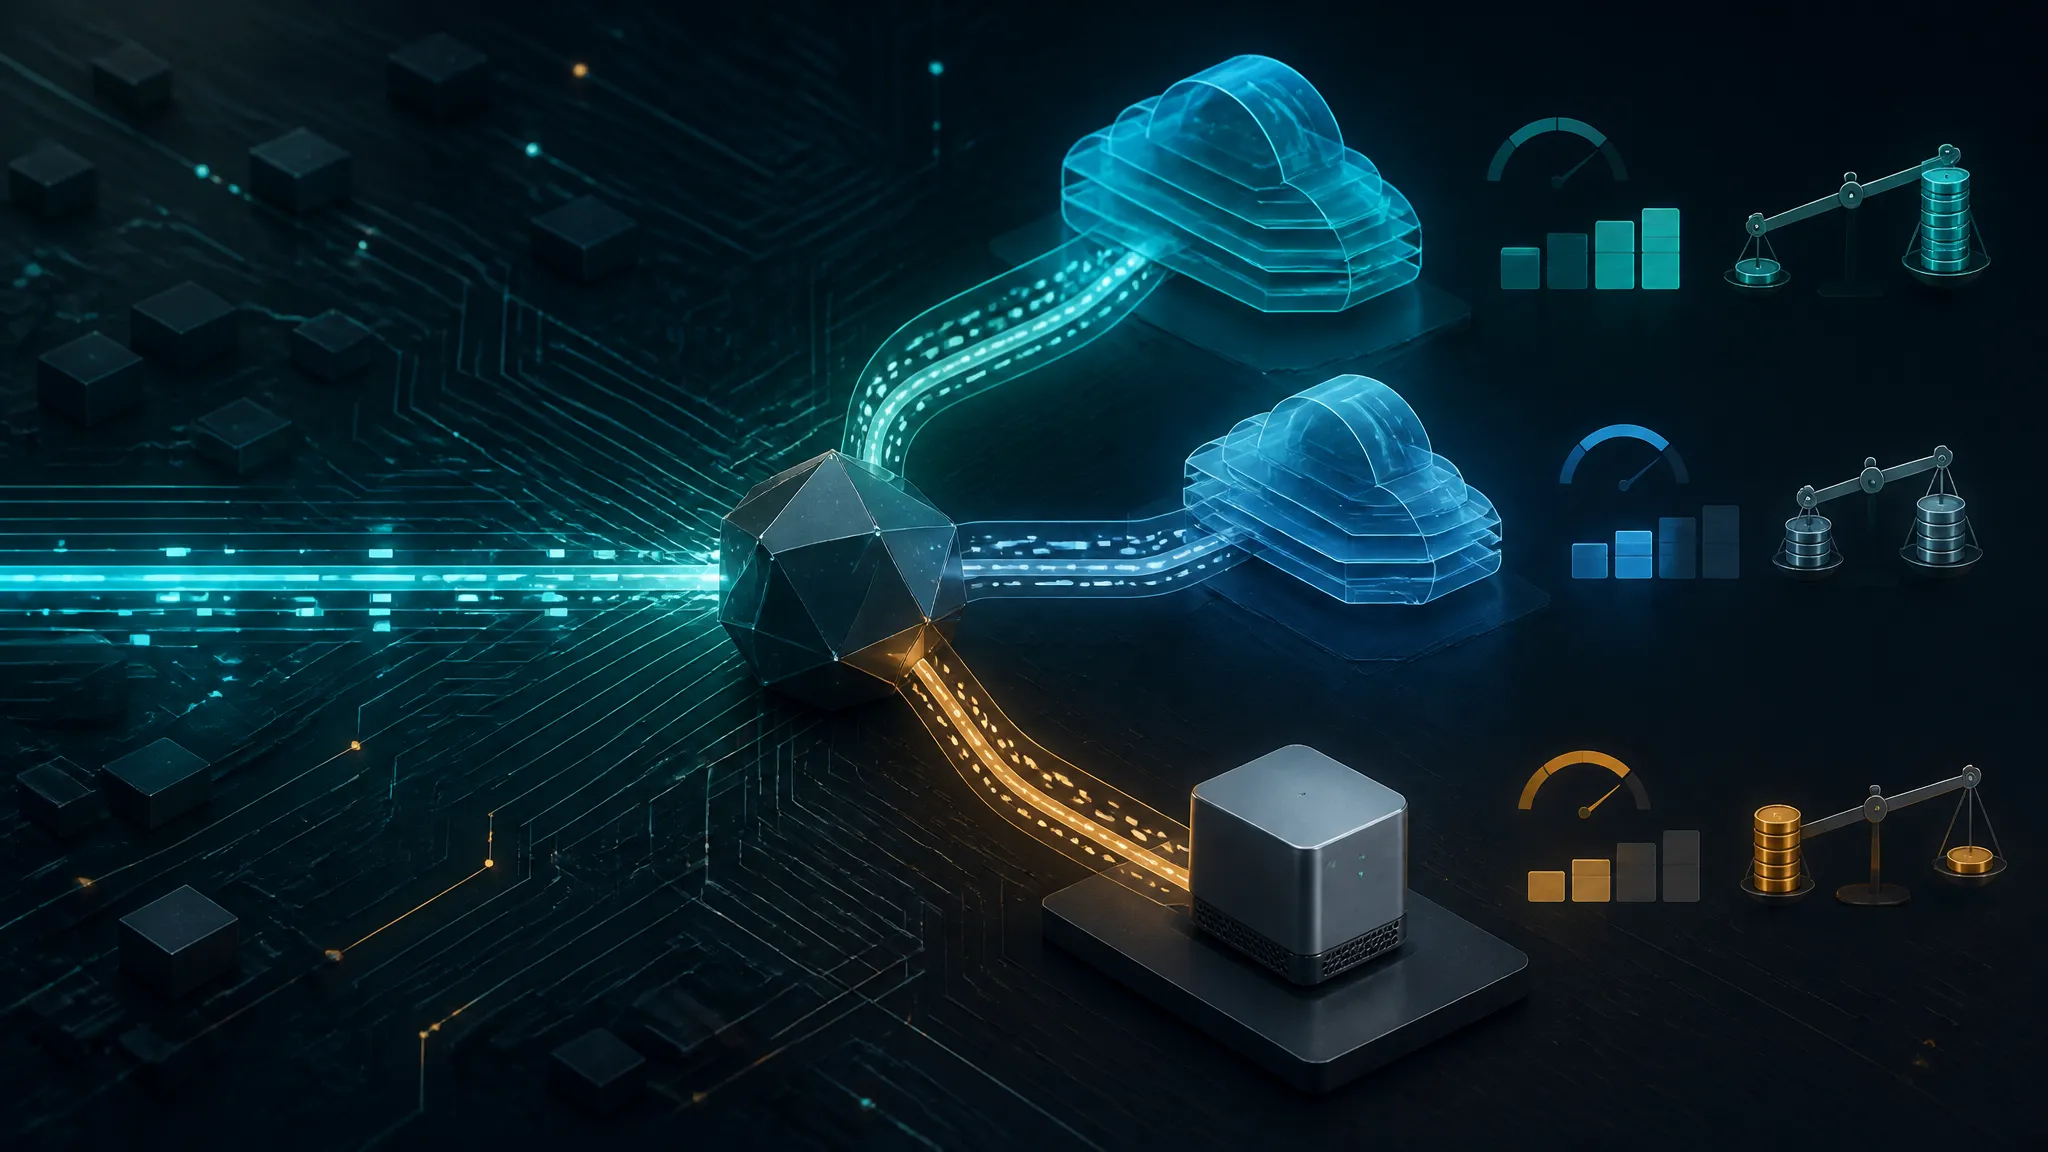
Build a cost-aware JavaScript router that sends each LLM request to a local Mac Mini model or the cheapest sufficient cloud tier based on prompt complexity, per-token price, and latency budget.

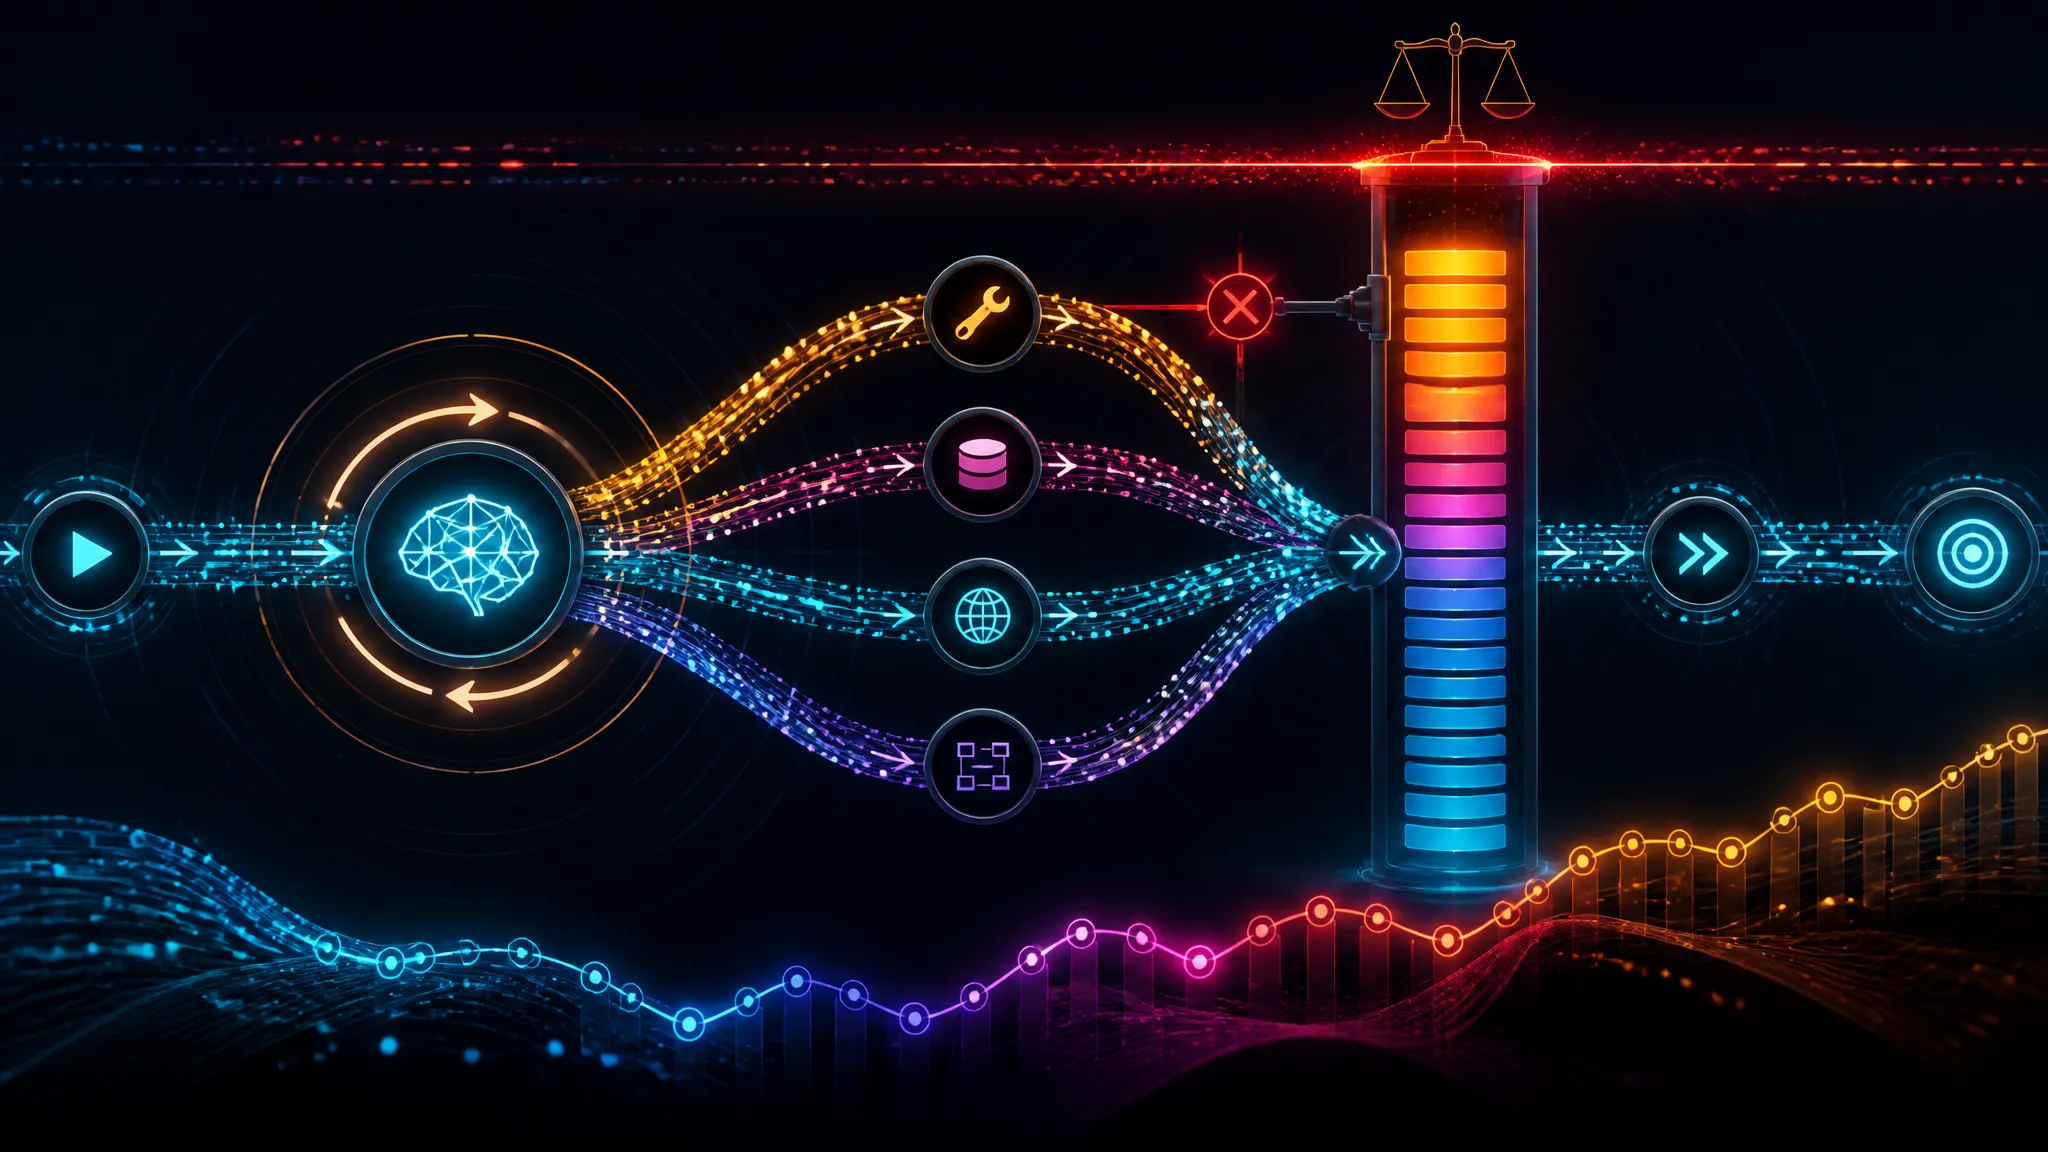
A hands-on guide to instrumenting JavaScript AI agents with per-step token accounting, cost tracing, and hard budget limits so you can measure real tokens-per-task instead of guessing from aggregate usage.

With Node 20 removed from GitHub Actions runners, this guide walks through updating action.yml from runs.using: node20 to node24 — rebuilding the bundled toolchain, refreshing dependencies, retesting inputs and outputs, and cutting a release that keeps existing workflows green.

A technical walkthrough of the malicious Axios npm release shows exactly how a postinstall hook escalates from a dependency install into remote code execution inside CI pipelines, and which lockfile and install-script signals developers should audit first.

A hands-on audit guide covering how publicly reachable Vite dev servers leak .env secrets and cloud credentials through the /@fs file-read endpoint and the HMR WebSocket, along with the binding, firewall, and rotation fixes that close the exposure.

A developer-focused analysis of phishing pages that mutate their JavaScript on every load and how a runtime monitor can help detect and inspect the behavior.

A developer-focused analysis of the critical isolated-vm vulnerability that allowed untrusted JavaScript to escape its sandbox and execute code on the host.

This post examines code-level indicators that can help developers spot MessiahGPT-generated malicious JavaScript embedded in package supply chains and respond before it reaches production.

A practical guide for JavaScript backend developers on assessing exposure, patch priorities, and defensive testing strategies after Microsoft’s July 2026 Patch Tuesday disclosed CVE-2026-56155 and CVE-2026-56164 among 569 fixes.

Learn how to audit your npm pipeline after the jscrambler compromise by checking dependency integrity, install scripts, and developer exposure across your build process.

An analysis of the hardest defensive challenges JavaScript teams face when protecting apps from fully autonomous AI attackers, with practical security implications for modern web stacks.

A practical security-focused look at how attackers are abusing vulnerable e-commerce checkout JavaScript and how developers can audit, detect, and harden exposed storefront code.

A practical security analysis of how attackers used fake Cisco AnyConnect and Google Update installers with JavaScript-based delivery to drop SharkLoader and evade scrutiny.

A developer-focused analysis of how the Bajaj Auto breach underscores the need to harden JavaScript APIs and dependencies against supply chain attacks.

The first AI-built zero-day signals a new era of automated attacks that JavaScript frontend teams must address with stronger supply-chain, runtime, and dependency defenses.

An analysis of the Mastra npm supply-chain incident with practical checks developers can use to detect dependency hijacking before malicious packages reach production.

Build a real-time QR code phishing detection workflow in JavaScript using the Safe Browsing API to flag malicious links before users scan them.

A practical hardening checklist for JavaScript developers responding to the actively exploited Chrome CVE-2026-11645 0-day and the broader critical fixes shipped in Chrome 149.

A deep technical walkthrough of the June 2025 Microsoft Patch Tuesday disclosure, focusing on the JavaScript and .NET remote code execution vulnerabilities, their likely impact paths, and the immediate patching priorities for developers and security teams.