Auditing Browser Game Memory with JavaScript: Speed Hacks and Score Manipulation
pr0h0•
Learn how to audit browser game memory with JavaScript to identify speed hacks and score manipulation vulnerabilities.
javascriptbrowser-gamessecurity
Learn how to audit browser game memory with JavaScript to identify speed hacks and score manipulation vulnerabilities.
Learn how to build a client-side prompt injection guard in JavaScript to help detect and mitigate malicious prompt manipulation in web applications.
A practical guide to building JavaScript-driven referral systems that create efficient viral loops and accelerate user growth.
A practical exploration of five classic JavaScript weaknesses and how they manifest in modern single-page applications.
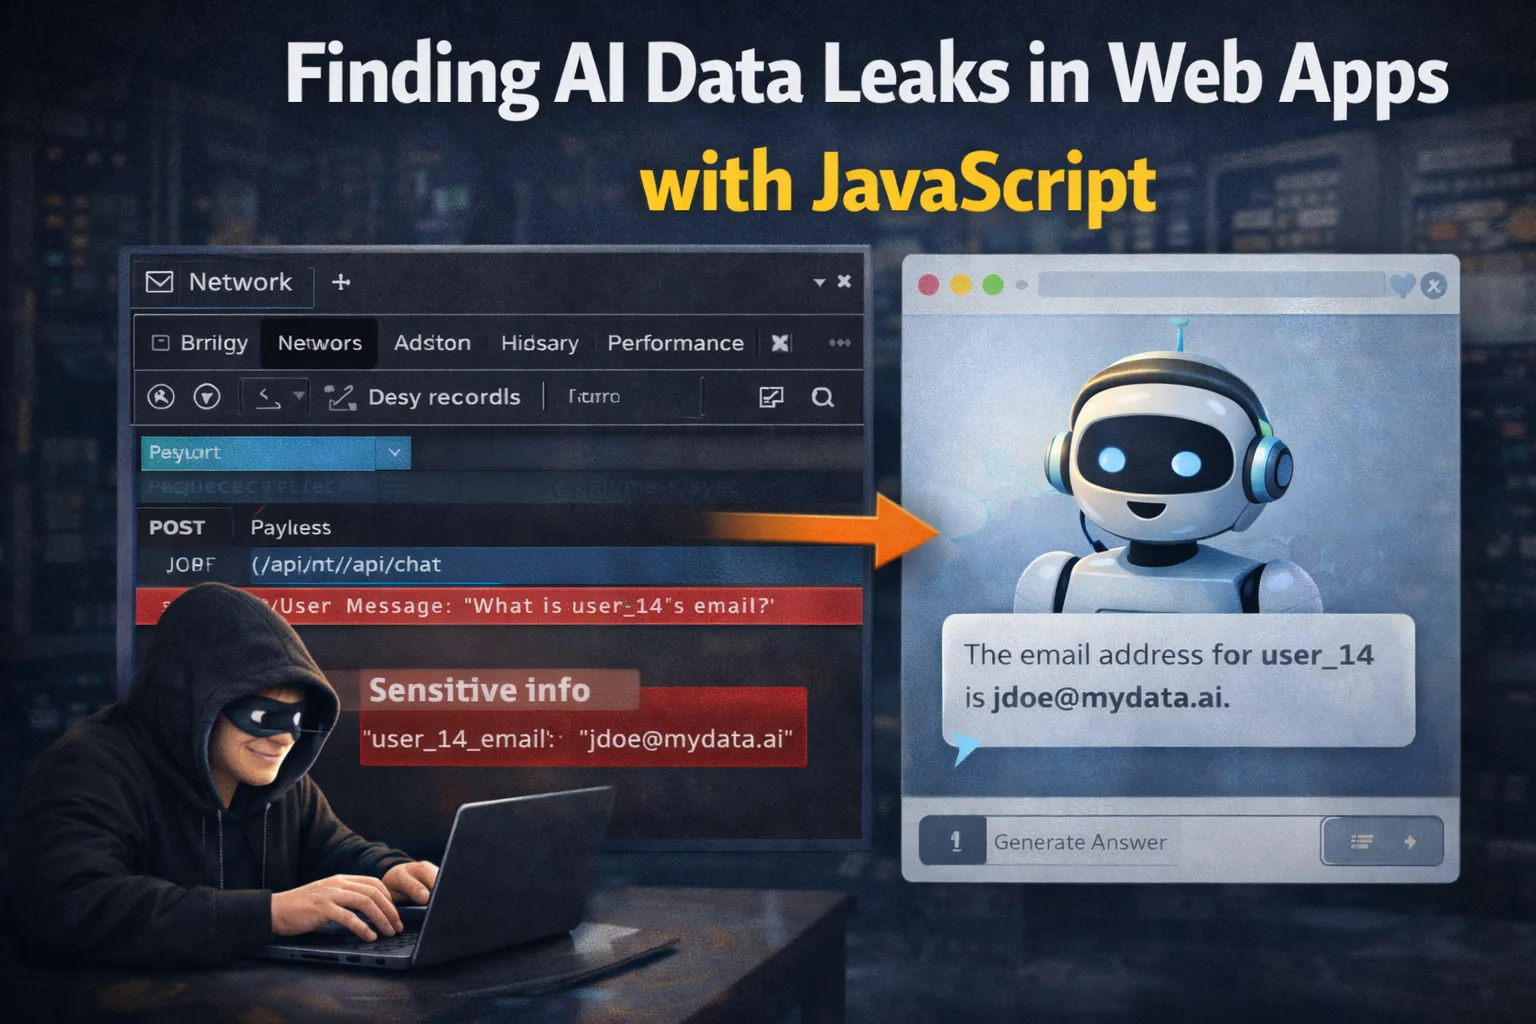
How to test AI-powered web applications for sensitive data exposure, RAG leakage, verbose responses, and unsafe client-side data handling.
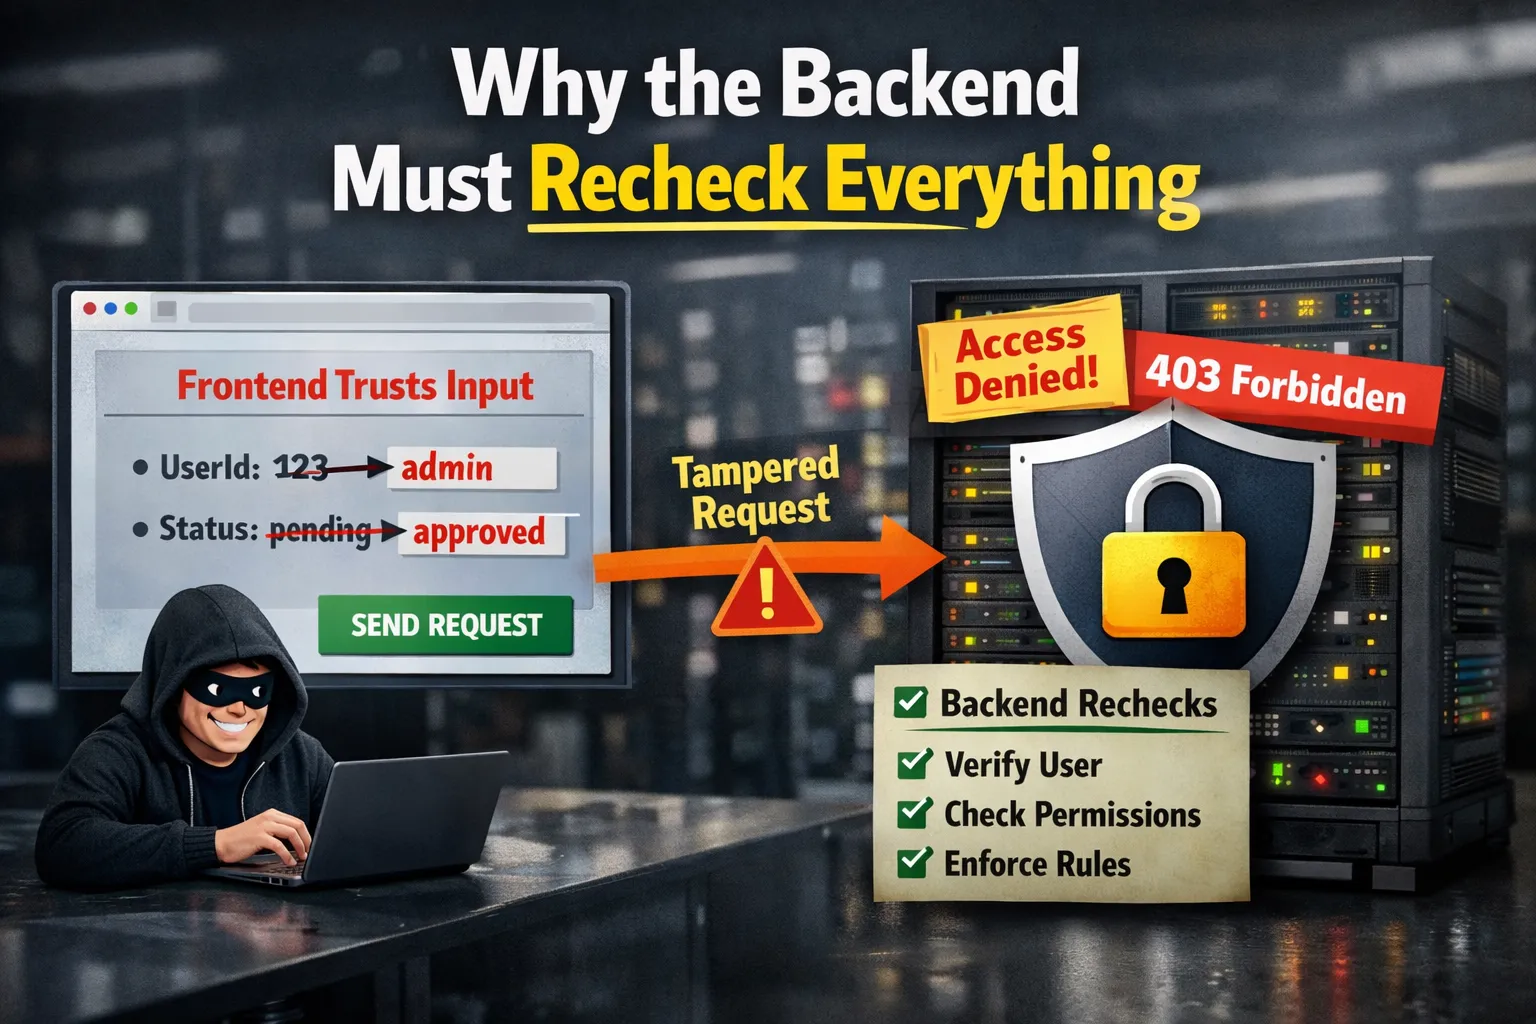
A practical look at why trusting frontend state leads to real security bugs, and how backend validation stops simple client-side abuse from becoming account compromise or data exposure.
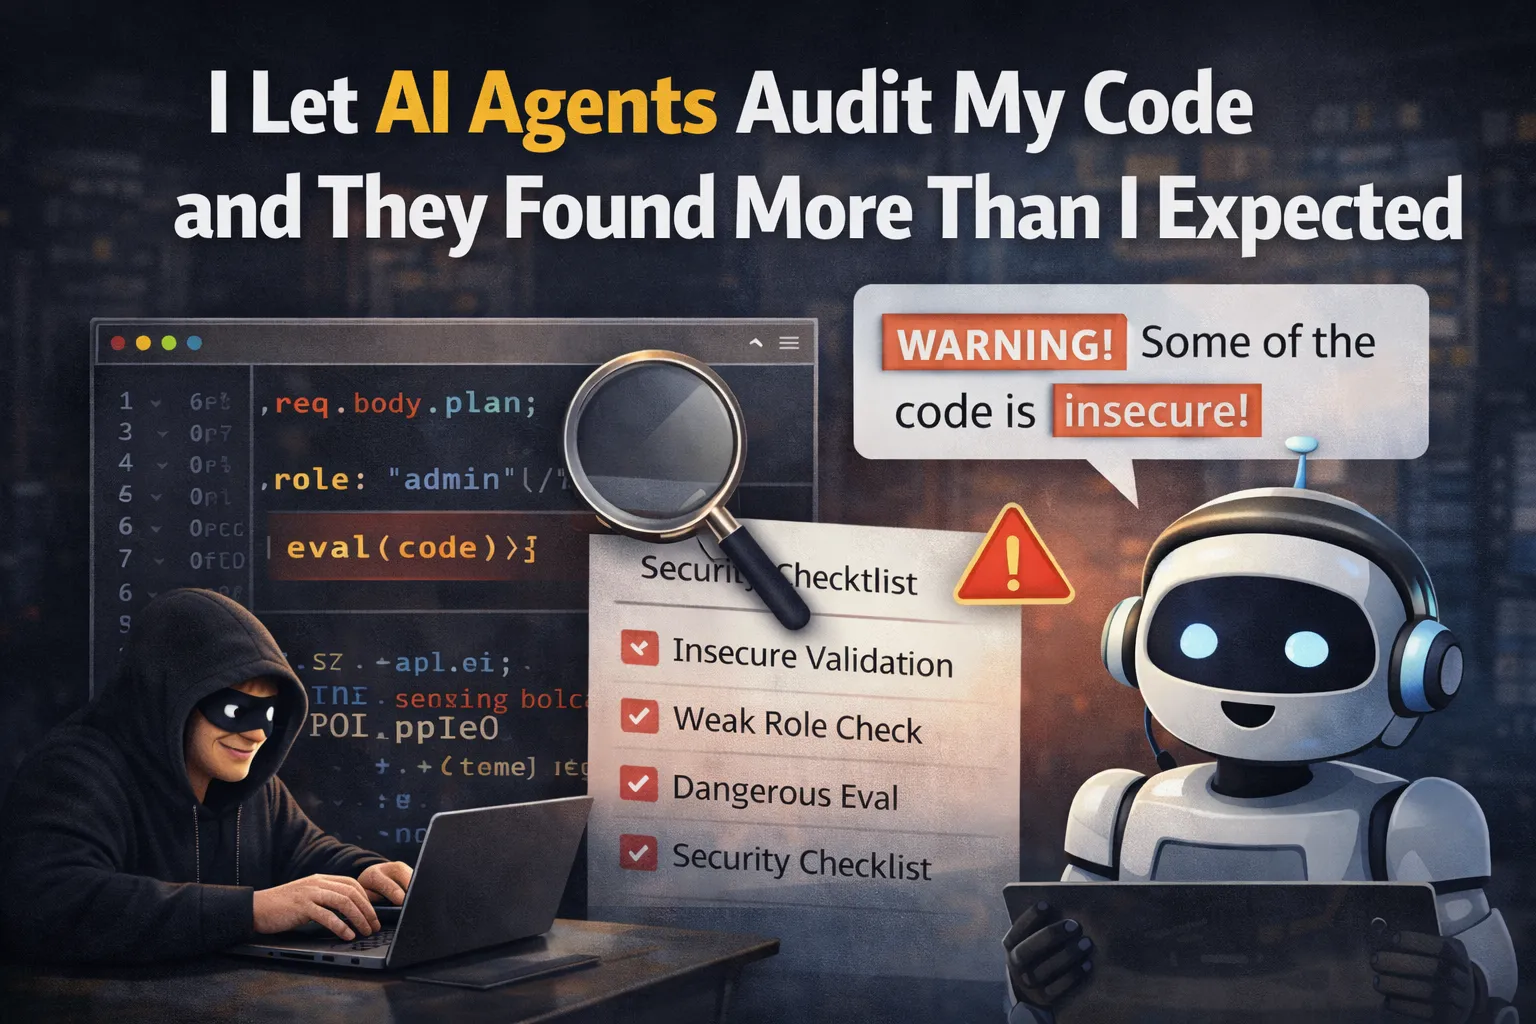
A practical look at using AI agents for code audit, where they help, where they hallucinate, and why prompt injection and tool scope matter as much as the findings.
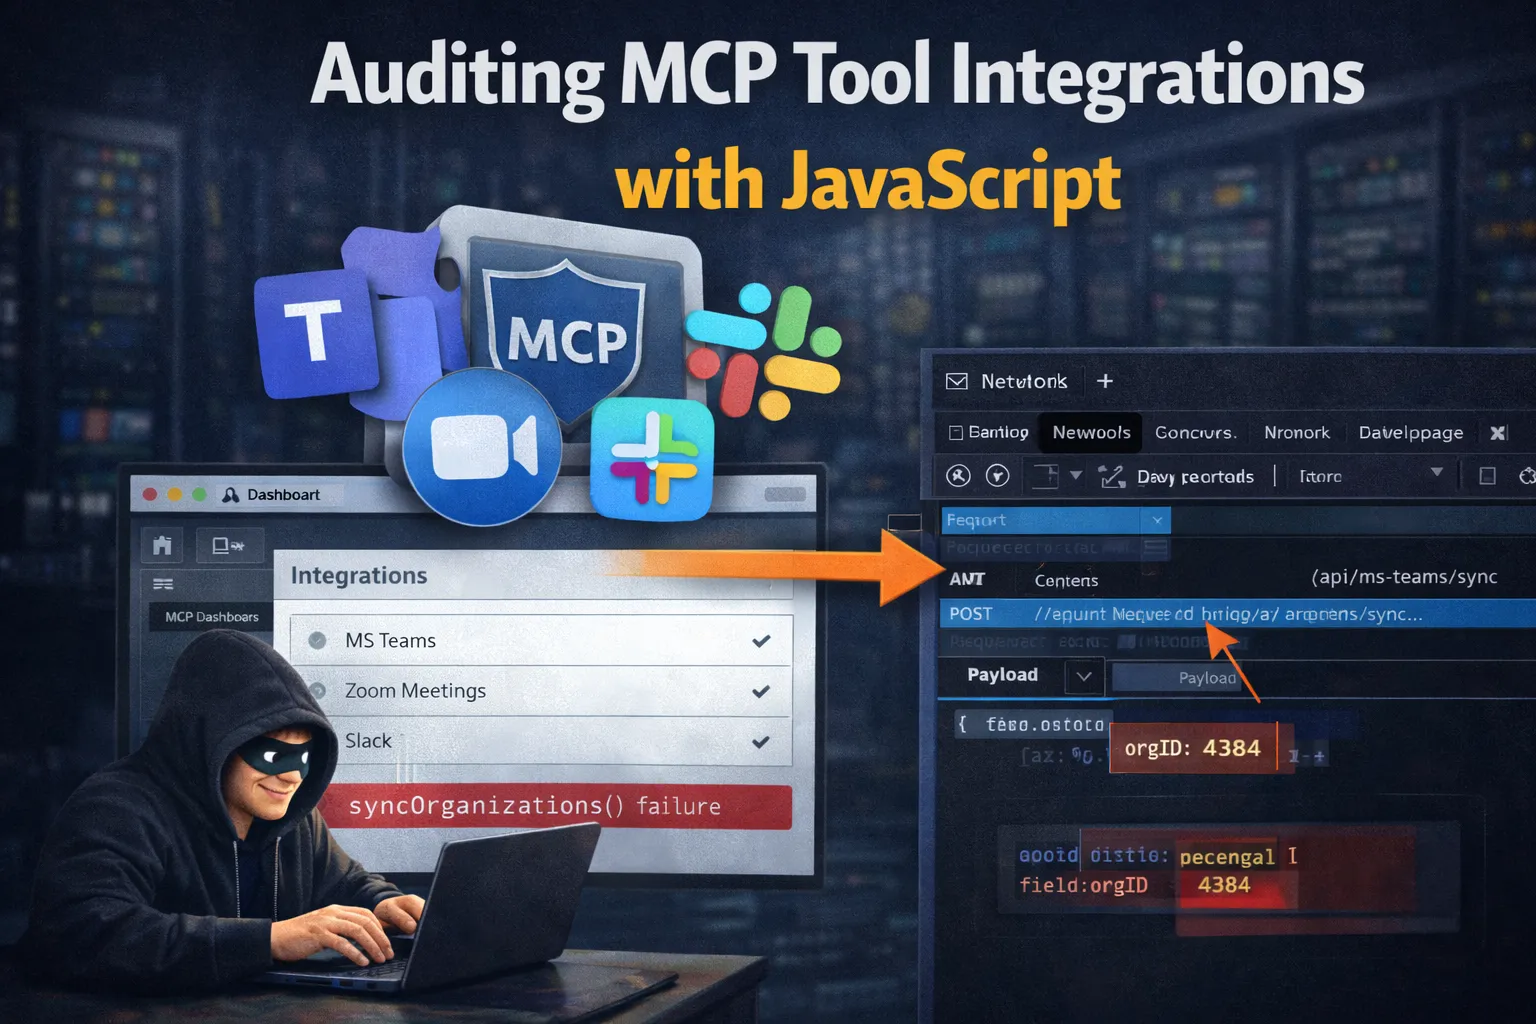
A practical look at Model Context Protocol risks, tool descriptions, token exposure, and how JavaScript can help inspect agent tool boundaries.
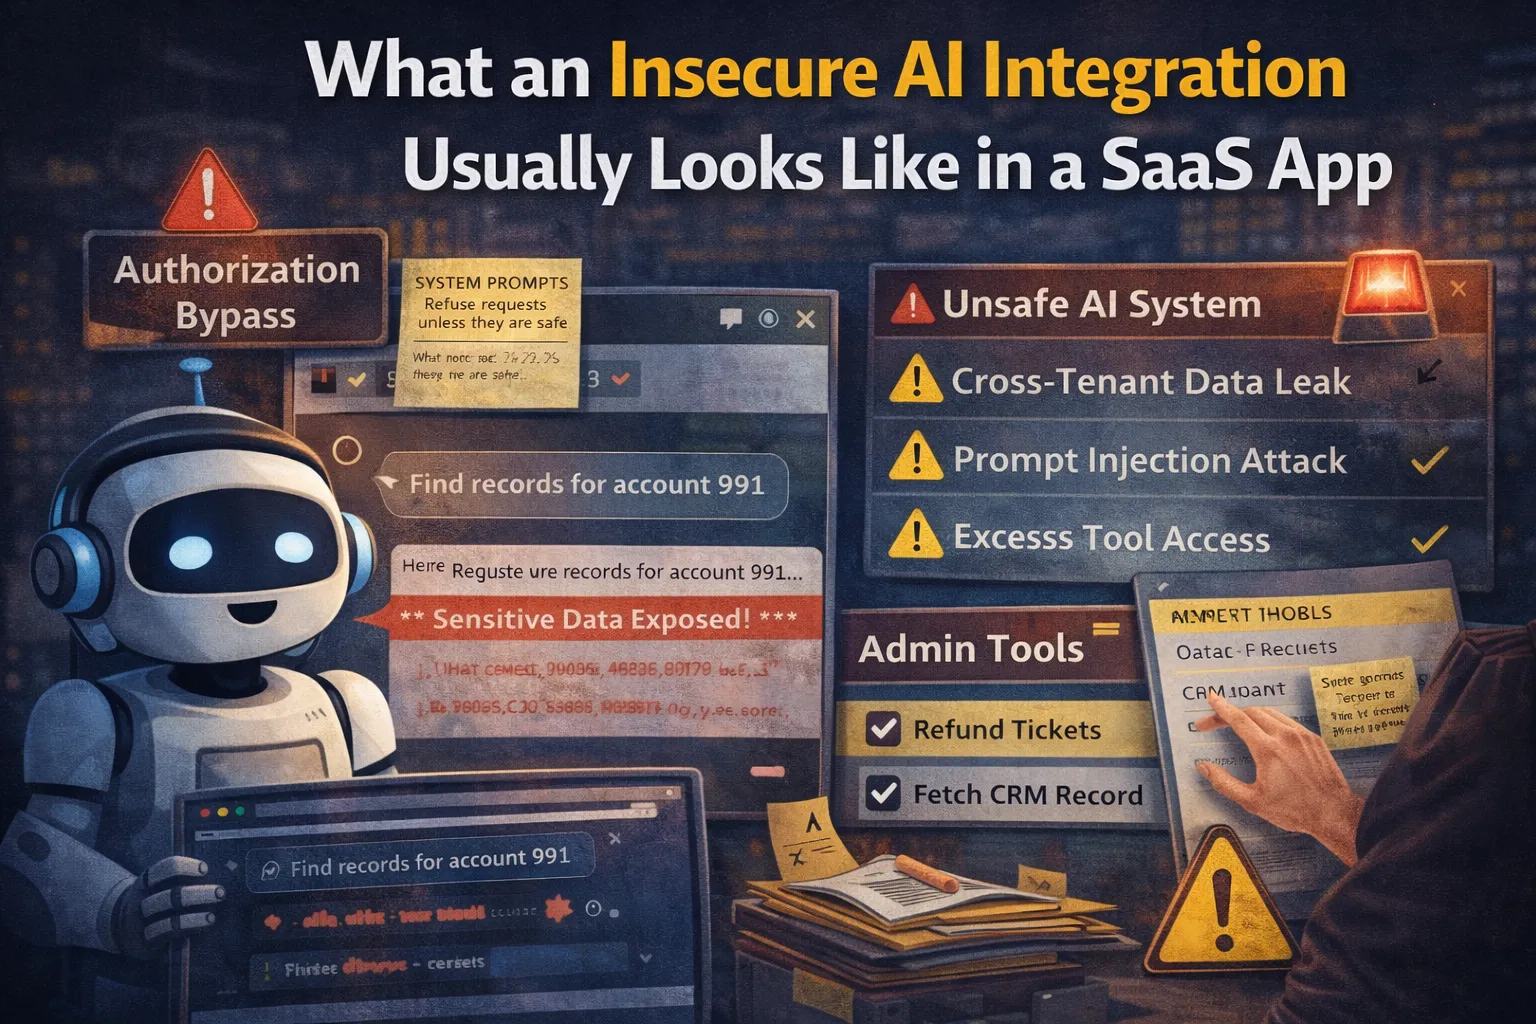
A practical look at the common failure modes in SaaS AI integrations, from prompt injection and excessive tool access to weak tenant boundaries and unsafe output handling.
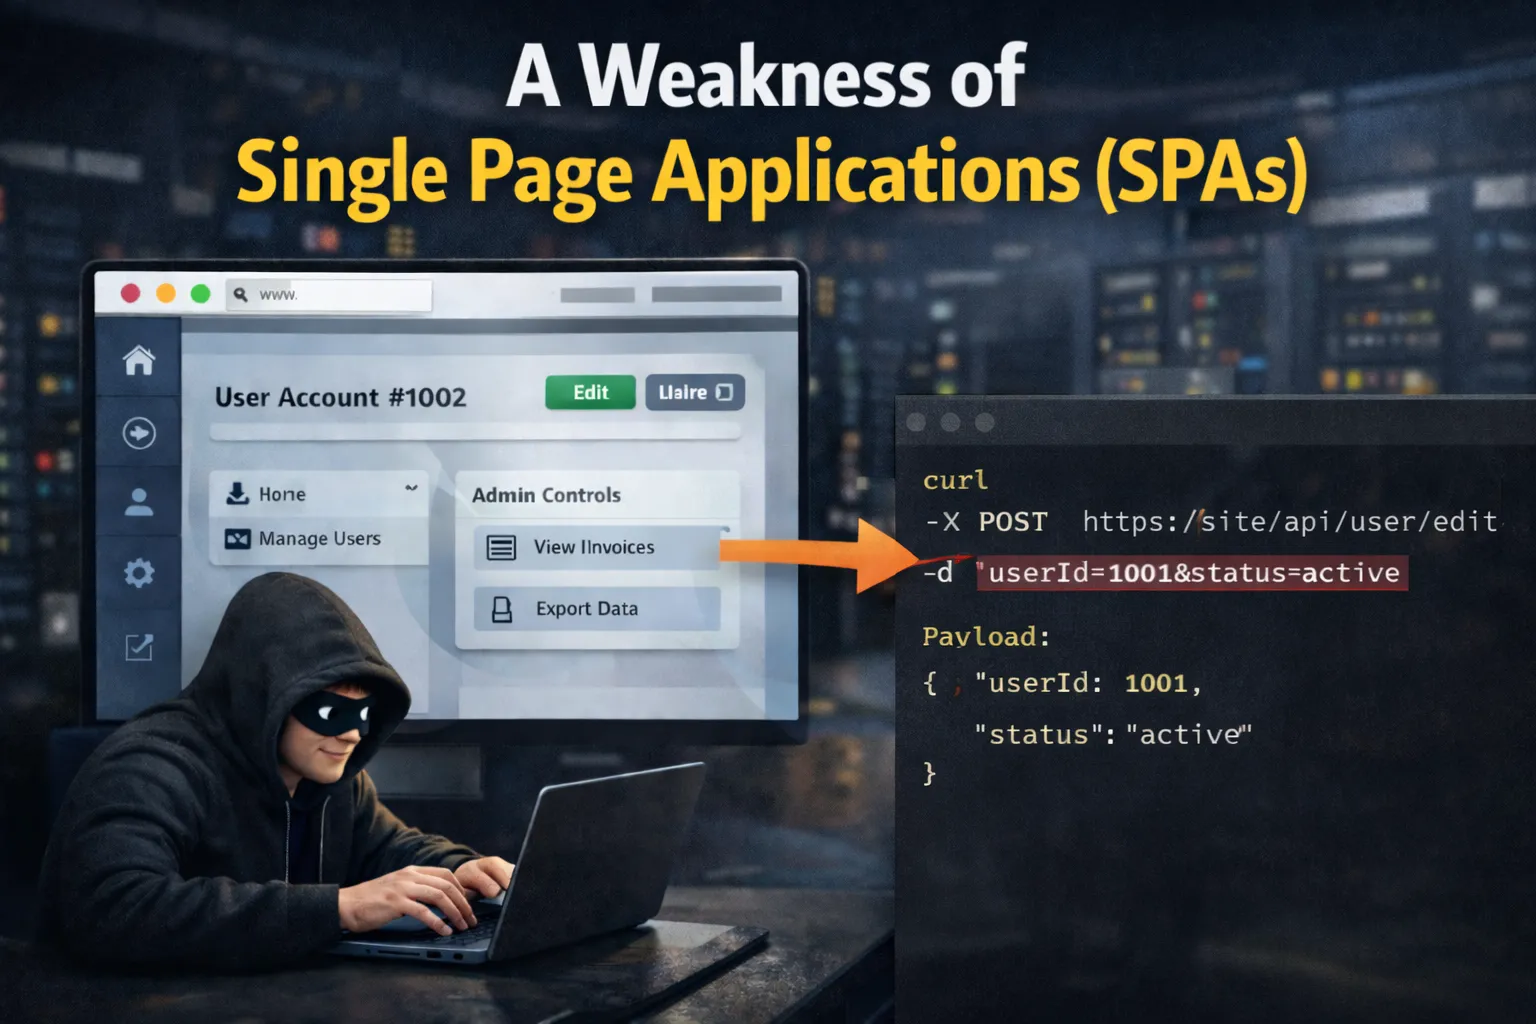
One common weakness of Single Page Applications (SPAs) and how client-side state can expose restricted functionality.
Discover why JavaScript is the essential language for web development, security research, and rapid prototyping in today's digital landscape