What the Cyber Resilience Act Actually Requires From a Release Pipeline
Map the EU Cyber Resilience Act’s vulnerability disclosure, security update, and SBOM requirements onto CI/CD pipelines and dependency-management tools.

Map the EU Cyber Resilience Act’s vulnerability disclosure, security update, and SBOM requirements onto CI/CD pipelines and dependency-management tools.

A practical audit guide for teams assessing cross-border AI dependencies and compliance checks after China's new export-license requirement for large AI models.

A developer-focused walkthrough of how the EU AI Act's risk tiers translate into concrete engineering obligations — model documentation, audit trails, human-in-the-loop gates, and incident reporting — when shipping agentic AI features.

This article explains the core engineering principles that make audit trails reliable, tamper-resistant, and useful for compliance, debugging, and accountability.

Explore what buyers notice when security answers are vague and how clarity can improve trust during evaluation.

Explore how Compliance as Code shifts teams from manually gathering audit artifacts to automatically generating trustworthy evidence throughout the software delivery lifecycle.

Security certifications like SOC 2 and ISO 27001 can help businesses build trust, meet buyer requirements, and expand into new markets.

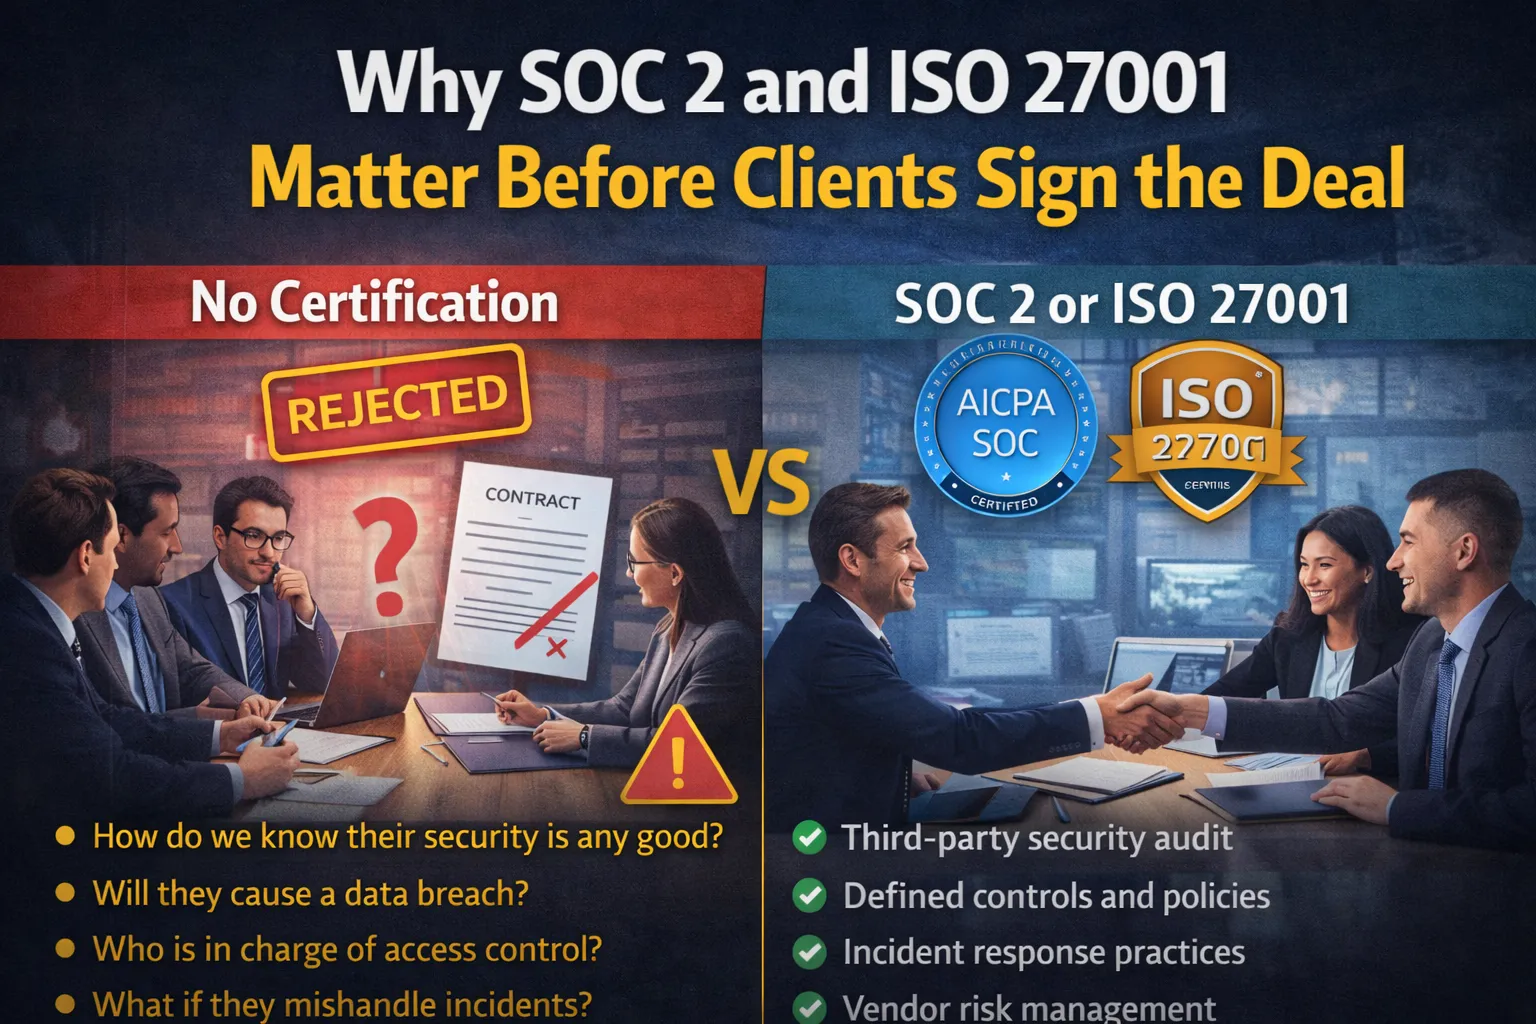
A practical look at why SOC 2 and ISO 27001 keep showing up in sales cycles, vendor reviews, and security questionnaires before a client will trust your company.