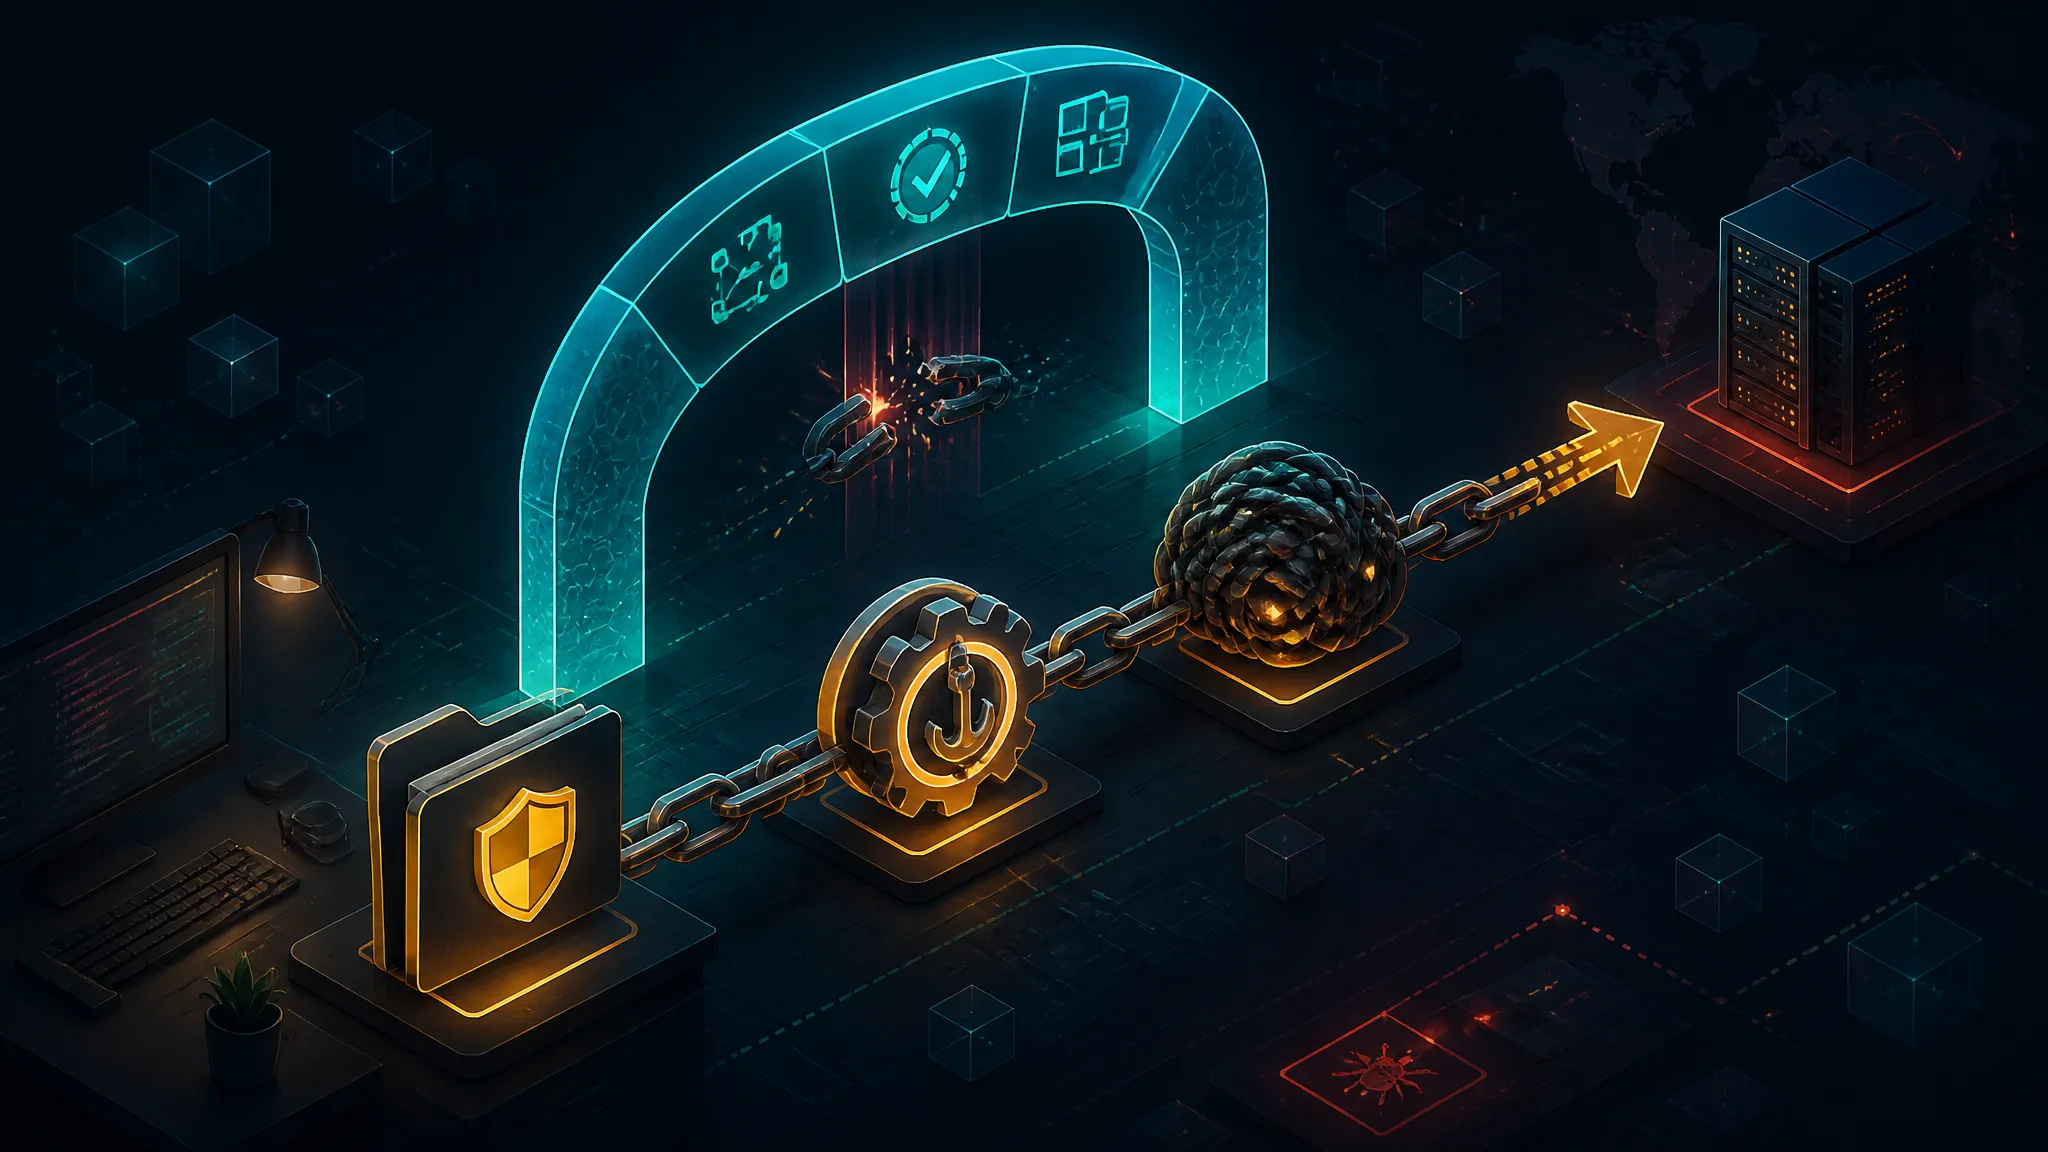
Dissecting a Fake Security Scanner Repo: postinstall Hooks, Obfuscated Loaders, and Exfil Endpoints
pr0h0•
A repo-level teardown of a fake GitHub "security scanner" that chains a postinstall hook, an obfuscated loader, and an exfiltration endpoint into a developer-targeted backdoor, with the install-script and CI controls that expose it before it runs.
supply-chain-securitymalware-analysisnpm