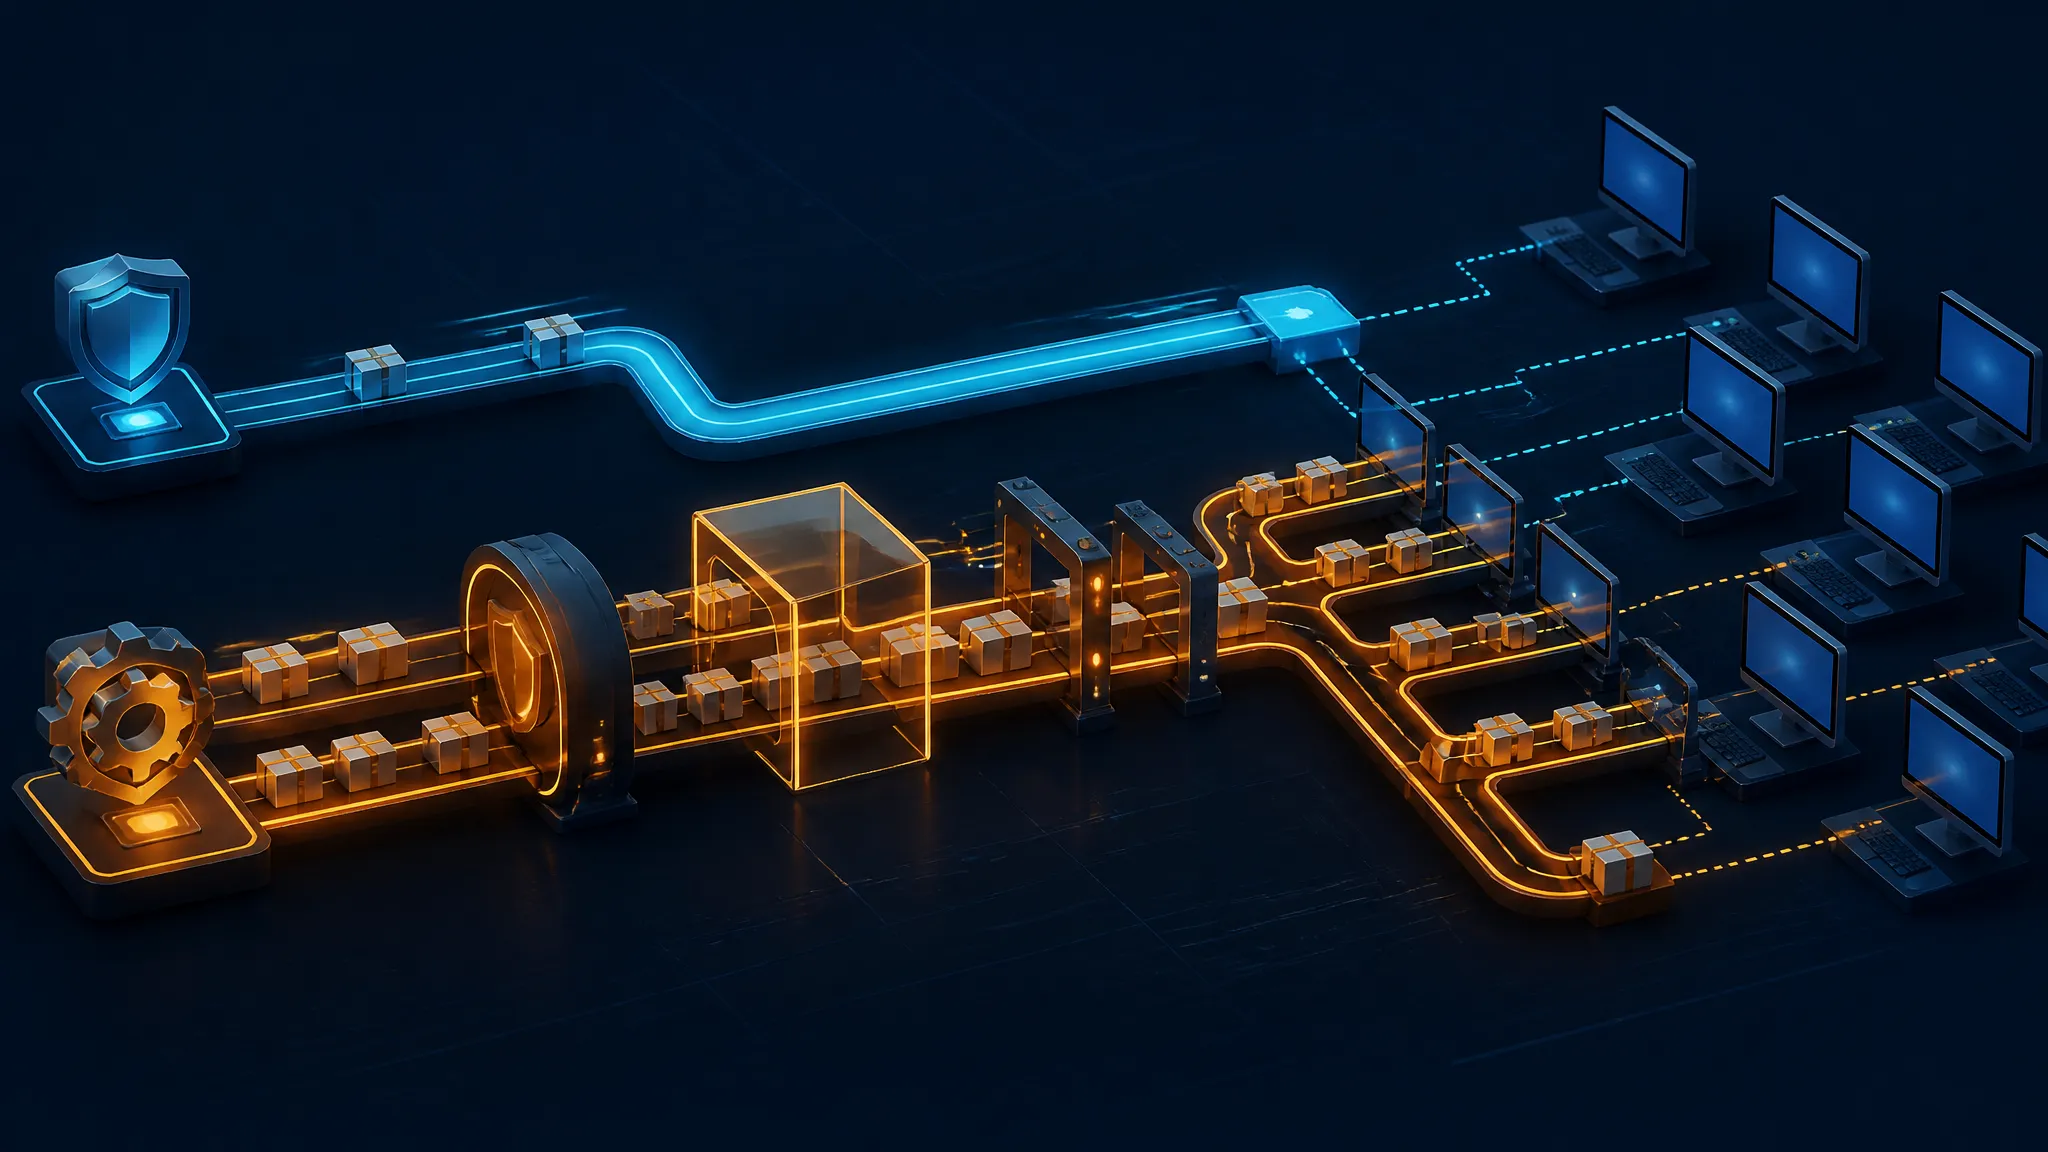
Windows Update vs. Third-Party Update Channels: Where Emergency Patch Delay Comes From
On this page
An Emergency Fix Is Not the Same as an Emergency Deployment
Time to Protection Is the Only Number That Matters
A finished fix is not a deployed fix, and the distance between them is where emergency patch delay actually comes from. This article compares the Windows Update servicing path against the main third-party update channels — vendor self-updaters, the Microsoft Store, WinGet, and enterprise software distribution — and shows how to measure the delay at each handoff instead of reading it off a press release.
Between "engineering signed off" and "the vulnerable binary is gone from the fleet" there is packaging, signing, channel publication, device applicability, download, installation, and — for a large share of Windows changes — a restart. Every step is a queue with an owner, and announcement timestamps measure none of them.
The headline framing around this topic invites a comparison of press-release dates, which is the wrong comparison. A vendor can publish a fixed build on day one and still leave endpoints exposed on day twenty, because what actually reduces risk is verified protection coverage, not publication. Track publication latency alone and you will declare victory while your exposure window is still open.
The useful measurement is a pair: publication latency (start → artifact available in its channel) and protection latency (start → target population verified on the fixed version). A release can win the first and lose the second.
What the MarketScale Listing Does and Does Not Say
The supplied source is a MarketScale listing dated 21 November 2026, syndicated through a Google News RSS entry. The headline is "Why Microsoft patches Windows in two days but makes third-party apps wait," with a one-line summary comparing a reported two-day Windows patch turnaround against longer waits for third-party applications.
That is the whole of what I was given. The excerpt names no specific vulnerability, no CVE, no Windows build, no third-party application, no distribution route, and no measured deployment population. It does not define "two days" — fix-to-publish, fix-to-general-availability, or publish-to-install are all plausible. It does not say how the third-party comparison was sampled.
Confirmed from the source: a two-day Windows figure and a longer third-party figure are asserted. Not established: any mechanism, affected software, or methodology. Everything below that explains why such a gap might exist is mechanics and inference, labelled as such — not a restatement of the listing's findings.
The Position: Platform Ownership Shortens Handoffs, Not Physics
Platform ownership of an operating system reduces the number of independent organizations that must each agree before bytes reach an endpoint. Microsoft controls the servicing branch, the package format, the signing infrastructure, the distribution channel, and the applicability logic. That vertical integration collapses several organizational handoffs into internal ones, and an out-of-band release can bypass the monthly schedule.
The stronger version of the claim — Windows patches are universally faster — does not survive contact with the mechanics, and the idea that third-party software universally waits on Microsoft approval is wrong as a general statement. Most desktop software distributed by direct download is never reviewed by Microsoft. A Store-distributed app goes through certification. A WinGet manifest points at a vendor-hosted installer Microsoft does not gate. Three different pipelines with three different bottleneck profiles, lumped together under the headline's "third-party apps" label. That lumping is the analytical error.
Define the Patch Clock Before Comparing Delivery Speed
Seven Milestones Between Discovery and Protection
Any credible comparison fixes the clocks first. I use seven milestones and won't compute anything until all seven exist:
- Discovery — the vulnerability is known to the party that will fix it.
- Fix ready — the code change is merged and unit-tested in the maintainer's tree.
- Artifact signed — a distributable, authenticated build exists.
- Channel available — the build is retrievable by the intended population.
- Device offered — applicability logic has actually surfaced the update to a given endpoint.
- Installed — the new bytes are on disk.
- Protection verified — the fixed code is running, the vulnerable path is no longer reachable, and the version is confirmed on the endpoint.
Protection verification is not pedantry. On Windows, an installed file that a running process still has mapped is not remediation. For a desktop app, a staged update that applies on next launch is not remediation either. And "channel available" is arguably the least meaningful of the seven for risk purposes — it is the milestone the vendor fully controls and the one the attacker does not care about.
A Milestone Table With Owners and Evidence
| Milestone | What it proves | Accountable party | Evidence to retain |
|---|---|---|---|
| Discovery | Clock starts | Reporter / vendor PSIRT | Advisory ID, internal ticket |
| Fix ready | Change exists | Product engineering | Merge commit, test run |
| Artifact signed | Distributable build exists | Release engineering | Signing log, artifact hash |
| Channel available | Retrievable | Distribution / store ops | CDN publish record, manifest version |
| Device offered | Applicability resolved | Platform servicing | Offer/eligibility report |
| Installed | Bytes on disk | Endpoint / MDM | Install record, file version |
| Protection verified | Running fixed code | Endpoint ops | Process version, post-restart check |
A couple of habits turn the table into a working tool. Record active work and queue time as separate columns — a three-day gap between "artifact signed" and "channel available" means very different things if a human was testing versus the package sitting in a certification queue. And track maintenance-window waits explicitly: in enterprise fleets, the single largest interval is frequently not a vendor at all. It is the gap between "offered" and "installed" imposed by an administrator's ring schedule.
Compare Like With Like, and Label What Is Missing
To compare two delivery paths honestly, hold these constant: vulnerability class and severity, supported version range, distribution route, deployment policy (forced vs. user-initiated vs. ring-based), and target population definition. If any differ, the latency numbers aren't comparable — say so rather than dividing them into a speed ranking.
For the MarketScale comparison, the gaps are precise: no severity class, no version range, no route, no policy, no population. That does not make the report wrong. It makes it unverifiable at the level of mechanism, which is exactly the level a release engineer needs.
What Microsoft Controls in the Windows Update Path
Tracing a Servicing Path From Fix to Restart
A simplified path for a supported-branch fix: the change lands in the servicing branch for each supported build; packages are constructed per architecture and per servicing stack requirement; the package is signed and validated against the applicability matrix; it is published to Windows Update and the Update Catalog; client-side applicability logic evaluates each device against prerequisites; the device downloads, stages, installs, and — for most kernel and servicing-stack changes — requires a restart to take effect.
The vertical integration shows in the middle of that chain. Package construction, signing, and publication are the same organization, on the same tooling, with the same release owners, for every supported build. No third party to negotiate a publish date with, no external artifact to re-verify. That is a real structural advantage, and it is the honest core of the "two days" claim: fewer handoffs, fewer places to wait.
What Out-of-Band Actually Changes
An out-of-band release moves publication outside the monthly cadence. That's a scheduling change, and scheduling is often the dominant term in the queue. It does not remove compatibility validation, servicing-stack prerequisites, or administrator policy. It also doesn't collapse "published" and "installed," which in a fleet with ring-based deployment can be days apart.
Worse, an out-of-band release can increase per-device latency risk because it lands outside the maintenance window change-management processes were designed around. The package shipped faster; the fleet may absorb it slower.
The Gates Microsoft Does Not Remove
These remain after publication, and this is where protection latency actually accumulates:
- Prerequisites. Servicing stack updates, licensing state, and build eligibility determine whether a device can even be offered the package.
- Deployment targeting. Windows Update for Business policies, ring assignments, and deferral settings decide who sees it and when.
- Rollout controls and holds. Safeguard holds can block an offer to a device segment while a known issue is investigated. This is a safety feature that directly adds latency, and it is a deliberate trade.
- Enterprise approval. Many organizations test before approving, regardless of what Microsoft publishes.
- Offline and intermittent devices. A laptop that is off for a week has an offer queue, not an installation.
- Restart behaviour. Active-hours settings and user deferrals can stretch install-to-effective across several days.
Not every update traverses every gate. Feature updates, servicing stack updates, Defender definition updates, and driver packages have materially different gates and cadences. Any model that assigns one latency number to "Windows updates" is already wrong.
The Real Advantage: Fewer Organizational Handoffs
Stated precisely, the advantage is coordination cost, not magic. Microsoft controls the OS, the servicing infrastructure, the signing authority, and the distribution channel, so an emergency path requires sign-off inside one organization rather than across three. That is a meaningful reduction in the variance of emergency releases, and variance is what hurts during an incident.
It is not a guarantee. Individual product teams still own their fixes, and enterprise administrators still own their rollout. A perfectly integrated pipeline that publishes on day two still produces day-ten protection if the customer's ring schedule says so.
Third-Party Software Has Several Different Update Paths
Four Distribution Routes Compared
| Route | Controls artifact | Controls metadata | Controls publication | Controls rollout | Controls install |
|---|---|---|---|---|---|
| Vendor self-updater | Vendor | Vendor | Vendor (own CDN) | Vendor defaults + user | App process |
| Microsoft Store | Vendor (packaged) | Partner Center | Microsoft certification | Microsoft + user | Store service |
| WinGet | Vendor (installer URL) | Manifest in winget-pkgs | Repository merge | User or admin command | Installer |
| Enterprise-managed | Vendor | Vendor + IT repackaging | IT | IT | IT (MDM/SCCM) |
Read the third column carefully: only one of these four routes involves Microsoft deciding when the artifact becomes available. In the self-updater route, Microsoft appears nowhere. In the WinGet route, Microsoft validates and merges a manifest — the installer itself is hosted by the vendor and isn't reviewed for safety. In the enterprise route, the customer is the publisher.
Discovery Is Not Delivery
Two distinctions get lost in these discussions.
A package in a repository does not mean an installed application will update. A WinGet manifest update makes a new version installable. It doesn't reach into an existing installation. If the app has no self-updater and the user never runs winget upgrade, the old version stays. That's a discovery improvement, not delivery.
A Store-distributed app is not governed like a directly downloaded installer. The Store route adds certification — a genuine gate with its own queue — in exchange for managed delivery. The direct-download route drops certification entirely and pushes the trust decision onto the user or the enterprise. Neither is universally faster; they fail in different places.
Route-Specific Queues in Third-Party Update Channels
- Vendor self-updater: release approval inside the vendor, CDN invalidation and staged rollout percentages, updater client compatibility, and the user's willingness to restart the app.
- Store: Partner Center submission, automated and manual certification checks, publish scheduling, Store client update cadence, and the user's auto-update setting.
- WinGet: manifest authoring, schema validation in CI, moderator review, repository merge, then local install — which only happens if something invokes it.
- Enterprise: vendor release, internal packaging or repackaging, pilot ring, change approval, broad ring, maintenance window.
The longest queue in the enterprise route is usually the last one, and the customer owns it — not any vendor.
The Question Worth Asking About the MarketScale Claim
The framing implies Microsoft gates third-party applications. The productive version of that question is narrower and answerable: which documented handoff delayed a particular release, and what evidence establishes Microsoft controlled it?
For a Store-distributed app, a certification queue would be the answer, and Partner Center submission history would prove it. For a self-updating app, the answer is internal to the vendor and Microsoft is irrelevant. For an enterprise fleet, the answer is in the customer's change tickets. Without one of those three artifacts, "Microsoft makes third-party apps wait" is a hypothesis, not a finding.
Signing, Reputation, and Store Certification Are Different Gates
What Authenticode Does and Does Not Assert
Authenticode signing establishes that a PE file was signed by the holder of a specific private key and hasn't been modified since signing, subject to certificate chain validation and, where present, timestamping. That is an integrity and provenance claim.
It is not a safety claim, a compatibility claim, or an authorization-to-deploy claim. A validly signed binary can be vulnerable, malicious, or the wrong version. The signature tells you who built these bytes and that nobody swapped them — exactly what you need for update-channel integrity, and exactly nothing about whether the update is a good idea.
Certificate Acquisition vs. Routine Signing
These are different problems and only one is an emergency risk.
Renewing or acquiring an OV/EV code-signing certificate involves identity validation and, for many CAs, hardware token or HSM requirements. Weeks-scale process, and it should never be on the critical path of an incident. Routine signing with an already-valid, already-provisioned setup is minutes.
The emergency bottleneck is almost always the second kind, and it's organizational: protected signing access lives with a small group, credentials sit in an HSM behind an approval workflow, and release approvals gate the signing call. During an incident the signing service is available but the people who can authorize its use are in a meeting. That pattern shows up in post-incident reviews far more often than an actual certificate expiry — though an unmonitored expiry is a genuinely nasty, entirely preventable variant.
Reputation and Certification Are Separate Mechanisms
Three things get conflated:
- Authenticode — cryptographic provenance of the artifact.
- SmartScreen reputation — a heuristic built from observed download and install telemetry, which affects user-facing warnings. A valid signature is one input; it is not a bypass. A brand-new signed binary from an unfamiliar publisher can still warn.
- Store certification — a policy and technical review applied to packages submitted to the Store, which is a publish-time gate.
Neither reputation nor certification is Authenticode, and — the point the headline gets wrong — certification is not a mandatory Microsoft review of every third-party desktop release. It applies to Store submissions. Direct downloads skip it entirely.
A reputation warning is not a security control and should not be treated as one. Attackers defeat it by waiting or by purchasing an established signer. Conversely, suppressing warnings during an emergency by telling users to click through is a habit that trains the exact behaviour phishing relies on.
Updater Trust Boundaries
If you're building an emergency lane, the trust boundary of your updater is now load-bearing. Four rules:
- Authenticate metadata, not just payloads. An attacker who can rewrite the version manifest can pin users to an old, vulnerable build indefinitely. Sign the manifest, and verify the signature before parsing it.
- Restrict signing authority. Emergency keys should be scoped and time-limited. A break-glass signer that can sign anything forever is a permanent liability acquired during a bad week.
- Define version-transition rules. Accept forward upgrades only by default. If downgrade is required for recovery, make it an explicit, separately authorized operation.
- Bind the update to the product identity. Validate the signer subject and the expected product name, not merely that some valid chain terminates somewhere.
Reproduce the Latency Calculation with a Small JavaScript Model
The Synthetic Latency Fixture
The fixture below is synthetic. Not MarketScale's data, not Microsoft's data, not a measurement of any real release. It exists to demonstrate the arithmetic and the validation discipline. Save it as latency-fixture.json alongside the script.
{
  "startUtc": "2026-01-05T00:00:00Z",
  "targetPopulation": "1,000 synthetic managed endpoints, online 8h/day, 30-day offer window",
  "releases": {
    "synthetic-windows-oob": {
      "label": "Synthetic A — Windows out-of-band servicing release",
      "milestones": {
        "fixReady": "2026-01-05T06:00:00Z",
        "artifactSigned": "2026-01-05T14:00:00Z",
        "channelAvailable": "2026-01-07T00:00:00Z",
        "deviceOffered": "2026-01-07T02:00:00Z",
        "installed": "2026-01-09T00:00:00Z",
        "protectionVerified": "2026-01-10T12:00:00Z"
      }
    },
    "synthetic-vendor-store": {
      "label": "Synthetic B — third-party vendor, Store-distributed build",
      "milestones": {
        "fixReady": "2026-01-05T05:00:00Z",
        "artifactSigned": "2026-01-05T12:00:00Z",
        "channelAvailable": "2026-01-06T18:00:00Z",
        "deviceOffered": "2026-01-06T20:00:00Z",
        "installed": "2026-01-10T04:00:00Z",
        "protectionVerified": "2026-01-10T08:00:00Z"
      }
    }
  }
}
The Latency Comparison Script
// latency-model.mjs — Node 18+, no third-party dependencies
// Compares publication latency with protection latency across two
// explicitly synthetic release timelines. No network, no writes.


const MILESTONES = [
"fixReady",
"artifactSigned",
"channelAvailable",
"deviceOffered",
"installed",
"protectionVerified",
];

function parseUtc(label, releaseId, value) {
if (typeof value !== "string") {
  throw new Error(releaseId + ": missing milestone " + label);
}
const ms = Date.parse(value);
if (Number.isNaN(ms)) {
  throw new Error(releaseId + ": unparseable timestamp for " + label + " (" + value + ")");
}
return ms;
}

function hours(ms) {
return Math.round((ms / 3600000) * 100) / 100;
}

function pad(value, width) {
return String(value).padEnd(width, " ");
}

function analyse(fixture, releaseId) {
const release = fixture.releases[releaseId];
if (!release) throw new Error("unknown release: " + releaseId);

const at = { start: parseUtc("startUtc", releaseId, fixture.startUtc) };
const marks = release.milestones || {};
for (const name of MILESTONES) {
  at[name] = parseUtc(name, releaseId, marks[name]);
}

// Reject fixtures whose clocks run backwards. A missing milestone is
// already fatal above; it is never treated as zero.
let previous = "start";
for (const name of MILESTONES) {
  if (at[name] < at[previous]) {
    throw new Error(releaseId + ": " + name + " precedes " + previous);
  }
  previous = name;
}

const stages = [];
previous = "start";
for (const name of MILESTONES) {
  stages.push({ from: previous, to: name, duration: hours(at[name] - at[previous]) });
  previous = name;
}

const longest = stages.reduce((a, b) => (b.duration > a.duration ? b : a));

return {
  releaseId: releaseId,
  label: release.label,
  publication: hours(at.channelAvailable - at.start),
  protection: hours(at.protectionVerified - at.start),
  stages: stages,
  longest: longest,
};
}

const fixture = JSON.parse(
readFileSync(new URL("./latency-fixture.json", import.meta.url), "utf8")
);

const results = Object.keys(fixture.releases).map((id) => analyse(fixture, id));

console.log("Target population:", fixture.targetPopulation);
console.log("Clock start (UTC):", fixture.startUtc);
console.log("");

for (const r of results) {
console.log(r.label);
console.log("  publication latency : " + r.publication + " h");
console.log("  protection latency  : " + r.protection + " h");
console.log(
  "  longest interval    : " + r.longest.from + " -> " + r.longest.to +
  " (" + r.longest.duration + " h)"
);
for (const s of r.stages) {
  console.log("    " + pad(s.from + " -> " + s.to, 42) + s.duration + " h");
}
console.log("");
}

const byPublication = [...results].sort((a, b) => a.publication - b.publication);
const byProtection = [...results].sort((a, b) => a.protection - b.protection);

console.log("Published first : " + byPublication[0].label);
console.log("Protected first : " + byProtection[0].label);
Expected Console Output
Running the script against the fixture above produces, deterministically:
Target population: 1,000 synthetic managed endpoints, online 8h/day, 30-day offer window
Clock start (UTC): 2026-01-05T00:00:00Z

Synthetic A — Windows out-of-band servicing release
  publication latency : 48 h
  protection latency  : 108 h
  longest interval    : deviceOffered -> installed (46 h)
    start -> fixReady                             6 h
    fixReady -> artifactSigned                    8 h
    artifactSigned -> channelAvailable            34 h
    channelAvailable -> deviceOffered             2 h
    deviceOffered -> installed                    46 h
    installed -> protectionVerified               36 h

Synthetic B — third-party vendor, Store-distributed build
  publication latency : 42 h
  protection latency  : 128 h
  longest interval    : deviceOffered -> installed (80 h)
    start -> fixReady                             5 h
    fixReady -> artifactSigned                    7 h
    artifactSigned -> channelAvailable            30 h
    channelAvailable -> deviceOffered             2 h
    deviceOffered -> installed                    80 h
    installed -> protectionVerified               4 h

Published first : Synthetic B — third-party vendor, Store-distributed build
Protected first : Synthetic A — Windows out-of-band servicing release
This is the whole argument in two lines of output. Synthetic B was available to the channel six hours earlier than Synthetic A and still reached verified protection twenty hours later. A report that measures publication latency would rank B as the faster release. The actual exposure outcome is the reverse: B's eighty-hour install interval — driven by a distribution route that doesn't force installation — dominates its timeline.
The practical lesson: the interval worth attacking was not signing, not certification, and not Microsoft. It was offer-to-install, which in this model belongs to the customer's deployment posture.
Limits of the Experiment
Be blunt about what this doesn't show. The arithmetic demonstrates a measurement method and a validation discipline. It says nothing about MarketScale's reported two-day turnaround, nothing about any real Microsoft or third-party release, nothing about your fleet. The timestamps were chosen to illustrate a shape, not to represent a sample.
To make it real, swap the fixture for authorized records: your vendor's advisory publication timestamp, your artifact signing log, your channel publish record, your MDM offer report, your install telemetry, your post-restart version verification. Keep the validation rules — missing milestones should fail loudly, because a milestone you can't find is a milestone you can't improve.
Inspect One Authorized Windows Endpoint Without Changing Its Update State
Read-Only PowerShell Collection
Every command below reads. None installs, approves, defers, or scans. Run it against a lab machine or a host you are explicitly authorized to inspect.
$ErrorActionPreference = 'Stop'
$cv = 'HKLM:\SOFTWARE\Microsoft\Windows NT\CurrentVersion'

[pscustomobject]@{
  CollectedUtc   = (Get-Date).ToUniversalTime().ToString('o')
  ComputerName   = $env:COMPUTERNAME
  OSVersion      = (Get-CimInstance -ClassName Win32_OperatingSystem).Version
  DisplayVersion = (Get-ItemProperty -Path $cv).DisplayVersion
  Build          = (Get-ItemProperty -Path $cv).CurrentBuildNumber
  UBR            = (Get-ItemProperty -Path $cv).UBR
} | Format-List
<#
Read-only inspection of one explicitly supplied application path.
Does not modify, launch, or update the application.
Save as an .ps1 file and invoke with -AppPath; a param() block
does not run when pasted directly into an interactive console.
#>
param(
[Parameter(Mandatory = $true)]
[ValidateScript({ Test-Path -LiteralPath $_ -PathType Leaf })]
[string]$AppPath
)
$ver = (Get-Item -LiteralPath $AppPath).VersionInfo
$sig = Get-AuthenticodeSignature -LiteralPath $AppPath
[pscustomobject]@{
Path = $AppPath
FileVersion = $ver.FileVersion
ProductVersion = $ver.ProductVersion
SignatureStatus = $sig.Status
SignerSubject = $sig.SignerCertificate.Subject
SignerThumbprint = $sig.SignerCertificate.Thumbprint
TimeStamper = $sig.TimeStamperCertificate.Subject
FileSha256 = (Get-FileHash -LiteralPath $AppPath -Algorithm SHA256).Hash
} | Format-ListIllustrative Output and What Each Line Establishes
The values below are illustrative placeholders, not a reading taken for this article. "Contoso" is a stand-in publisher.
CollectedUtc   : 2026-01-09T11:42:07.0000000Z
ComputerName   : LAB-WS-014
OSVersion      : 10.0.26100
DisplayVersion : 24H2
Build          : 26100
UBR            : <illustrative>
Path : C:\Lab\ContosoAgent\contoso-agent.exe
FileVersion : 4.12.3.0
ProductVersion : 4.12.3.0
SignatureStatus : Valid
SignerSubject : CN=Contoso Software Ltd, O=Contoso Software Ltd, C=GB
SignerThumbprint : <illustrative>
TimeStamper : CN=Contoso Timestamp Authority, O=Contoso Software Ltd, C=GB
FileSha256 : <illustrative>What each observation establishes:
- Build + UBR identify the servicing level of the OS. They don't tell you which specific fixes are present.
- FileVersion identifies the on-disk binary. Compare it against the vendor advisory's fixed-version threshold — and against the advisory's product and channel, because version numbers aren't globally unique.
- SignatureStatus = Valid establishes the file is intact and was signed by a chain that validates to a trusted root, with a countersignature present. It establishes nothing about the version being patched.
- TimeStamper matters more than people expect: without a countersignature, the signature becomes invalid when the signing certificate expires, which can break installer validation years later.
Blind Spots in Single-Endpoint Inspection
Get-HotFix reports what the Win32_QuickFixEngineering provider surfaces. Microsoft's documentation for that class has long described it as representing only a subset of the updates present on a system. Treat it as one signal among several, never as a complete servicing inventory.
Four more worth naming explicitly:
- A valid signature does not prove vulnerability remediation. It proves integrity.
- An updated file does not prove the running process loaded it. Check the loaded module version, not just the path on disk.
- A restart requirement may mean zero effective remediation until reboot. "Installed" and "protected" are different states, and pending-reboot is a real state to report.
- An unsigned file returns a null
SignerCertificate, so property access on it fails. Branch onSignatureStatusbefore reading signer fields.
A Defensible Verification Sequence
- Pull the vendor advisory and extract the fixed-version criteria verbatim, including the affected product editions.
- Confirm the endpoint is in scope: supported OS build, supported application edition, expected architecture.
- Record the on-disk version and hash.
- Record the running process module version (or the application's own version output) before and after relaunch.
- Confirm installation and restart records from your management plane, not from the application directory.
- Confirm post-restart that the fixed version is still what's running, and that the vulnerable code path is no longer reachable using the vendor's own reproduction criteria in an authorized lab.
- Keep release timestamps in a separate store from endpoint evidence. Mixing them is how organizations end up reporting publication time as if it were remediation time.
Engineer an Emergency Lane Without Removing the Safety Boundary
Prepare the Emergency Lane Before the Incident
Everything here should already exist when the incident starts. Building any of it during an emergency is how a bad week becomes a bad quarter.
- Reproducible release inputs: pinned dependencies, deterministic build, a tagged commit that maps to an artifact.
- Automated packaging and signing as a single command with a logged output hash.
- Protected signing access that a small on-call group can invoke without a meeting.
- Channel credentials and publish permissions tested quarterly, not annually.
- Representative test coverage for the install and upgrade paths, including the previous supported version.
- Named decision owners for promotion, with a documented fallback.
Classify Gates by Purpose
Treating gates as a flat list is why emergency processes either move too slowly or break things.
| Gate | Purpose | During an emergency |
|---|---|---|
| Artifact authentication | Integrity, provenance | Retain, always |
| Essential security checks | Prevent new exposure | Retain |
| Install/upgrade smoke tests | Prevent bricking | Retain, shorten scope |
| Explicit promotion authority | Accountability | Retain, pre-delegate |
| Broad regression suite | Quality | Shorten, defer remainder |
| Convenience scheduling windows | Calendar hygiene | Remove |
The rule: shorten discretionary scheduling waits, never integrity gates. An emergency release that skips signing verification has converted a patch into an attack vector with a friendly name.
Staged Deployment With Explicit Stop Criteria
Staging is not a slowdown if the criteria are written before rollout starts. Define up front:
- Expansion criteria — install success rate above a threshold, no new crash signature, no health signal regression, and version coverage confirmed on the pilot.
- Stop criteria — install failure rate above a threshold, any new crash cluster attributable to the build, or version coverage stalling while offer counts climb.
- Time box — a maximum pilot duration, so "waiting for confidence" cannot silently become the new bottleneck.
Measure verified fixed-version coverage as the primary metric, not install success. Install success measures whether your package works; coverage measures whether your exposure closed.
Recovery Depends on the Component
Recovery planning has to be component-aware, because "roll back" means different things and is sometimes unavailable.
- Distribution problem (bad manifest, wrong targeting): pause distribution and correct the channel. Cheap.
- Installer problem (fails on a configuration): stop the rollout, restore service with the prior package where supported, and ship a forward fix.
- Application problem (the fixed build regresses): forward fix is usually the only option, and the interim choice is between two bad states.
Rollback can reintroduce the vulnerability you just patched. For some changes — a schema migration, a certificate rotation, a service-side fix — rollback of the client is not a recovery path at all. Decide this before the incident, and record it in the runbook.
The Enterprise Operator's Half of the Job
Vendor publication does not complete remediation. Operators own a parallel lane:
- Preapprove emergency ownership. Name who can approve an out-of-band deployment, and their backup.
- Prepare deployment tooling. Test the push path and the reporting query before you need them.
- Communicate restart requirements to users with a real deadline and a real consequence.
- Track exceptions. Every device that did not install is an open risk item with an owner. An exception list that nobody reviews is a false assurance artifact.
- Reconcile coverage against the population definition. If your denominator shifts during the incident, your coverage number is fiction.
What Would Confirm the Report's Two-Day Comparison?
The Missing Primary Evidence
To move the MarketScale comparison from headline to finding, I'd need:
- The specific incident or advisory, with an identifier.
- Affected products and versions, on both sides of the comparison.
- Fix-ready and publication timestamps for each side.
- The third-party distribution route — self-updater, Store, WinGet, enterprise — because the answer changes completely across those four.
- Any documented approval wait, with the queue named and the timestamps.
- Endpoint coverage measurement, so protection latency can be computed rather than assumed.
None of these appear in the supplied excerpt. Not a criticism of the listing, which is a listing — a statement about what the listing can bear.
Confirmed Mechanics vs. Case-Specific Inference
Confirmed by primary documentation (the mechanism, not the case): Microsoft operates the Windows servicing, signing, and distribution pipeline for supported builds; out-of-band releases exist outside the monthly cadence; Authenticode provides integrity and provenance subject to certificate validation; Store submissions pass through certification; WinGet manifests reference vendor-hosted installers.
Inference (my reasoning, not established by any source I was given): the specific two-day figure most likely measures fix-to-publication rather than fix-to-protection; the third-party comparison most likely aggregated multiple distribution routes into one bucket; the dominant interval in most real fleets is offer-to-install rather than any vendor-side gate. Each is testable, none is proven here.
How the Conclusion Changes With the Evidence
| Evidence found | Conclusion it supports |
|---|---|
| Documented Store certification queue with dates | A channel-gate explanation for that case |
| Vendor packaging or signing delay, no external queue | The bottleneck was internal to the vendor |
| Enterprise pilot and change-approval records dominating | The customer owned the delay |
| A self-updater publishing in hours with high coverage | Contradicts any universal "Windows-first" ranking |
Only the first row supports the headline's implicit mechanism. The fourth row would refute the general claim while leaving the specific case intact.
Measure the Queue You Can Actually Shorten
Control of an operating system and its servicing infrastructure is a genuine operational advantage. Fewer organizational handoffs means less coordination variance during an emergency, and that's worth something real.
It's not a universal speed hierarchy. Most third-party desktop software never touches a Microsoft approval queue, and plenty of Windows updates reach protection days after publication because of gates Microsoft doesn't own. The two numbers that matter are publication latency and protection latency, and the second one usually determines your exposure.
So measure both. Instrument the seven milestones, refuse to treat missing ones as zero, report verified fixed-version coverage next to your publish timestamp. Then attack whichever interval is actually longest — because in a fleet of realistic size, that interval is often a maintenance window with your name on it.
Further Reading and Evidence Sources
The Supplied Listing
- MarketScale listing, "Why Microsoft patches Windows in two days but makes third-party apps wait" — supplied via Google News RSS, dated 21 November 2026. Secondary source, headline and summary only; no vulnerability, build, application, or population is identified in the supplied excerpt.
Primary Microsoft Documentation
- Windows release health — known issues, safeguard holds, and release status for Windows versions.
- Windows Update for Business: configure update deferrals — deployment rings, deferrals, and targeting policy that govern offer and install timing.
- Authenticode (Win32) — what code signing establishes about a PE artifact.
- SignTool — the signing and verification tool used for Windows artifacts.
- Get-AuthenticodeSignature — the read-only cmdlet used above.
- Get-HotFix — and its documented scope limits relative to a servicing inventory.
- Win32_QuickFixEngineering class — the provider behind
Get-HotFix. - Publish Windows apps and games — Partner Center submission and certification for Store-distributed packages.
- Windows Package Manager (WinGet) documentation — how WinGet manifests reference vendor installers.
- Microsoft Security Update Guide — advisories, severity, and affected-product metadata for Windows and Microsoft software.
More posts
Verifying WordPress 7.1.4 Core and Plugin Updates Against the Unauthenticated RCE
WordPress 7.1.4 ships fixes for 22 vulnerabilities including an unauthenticated RCE, and this walkthrough ranks them by exploitability and attack surface while giving a concrete core-update, plugin-audit, WAF, and post-patch integrity verification checklist.
An Out-of-Band Incident Channel for Teams Dependent on Microsoft 365 and N-able
A practical walkthrough for building an out-of-band incident channel that keeps teams communicating when Microsoft 365 or N-able disruptions take primary collaboration and alerting systems offline.
Testing Inkling 2 Mini’s Laptop Coding-Agent Claim with a Node.js Harness
Build a reproducible Node.js harness to independently test Inkling 2 Mini’s local coding-agent claims by measuring task completion, peak memory, end-to-end latency, and energy use against a conventional local model and hosted API.
Loading comments…