Auditing Third-Party Script Loads for Malware After a Tag Vendor Breach
pr0h0•
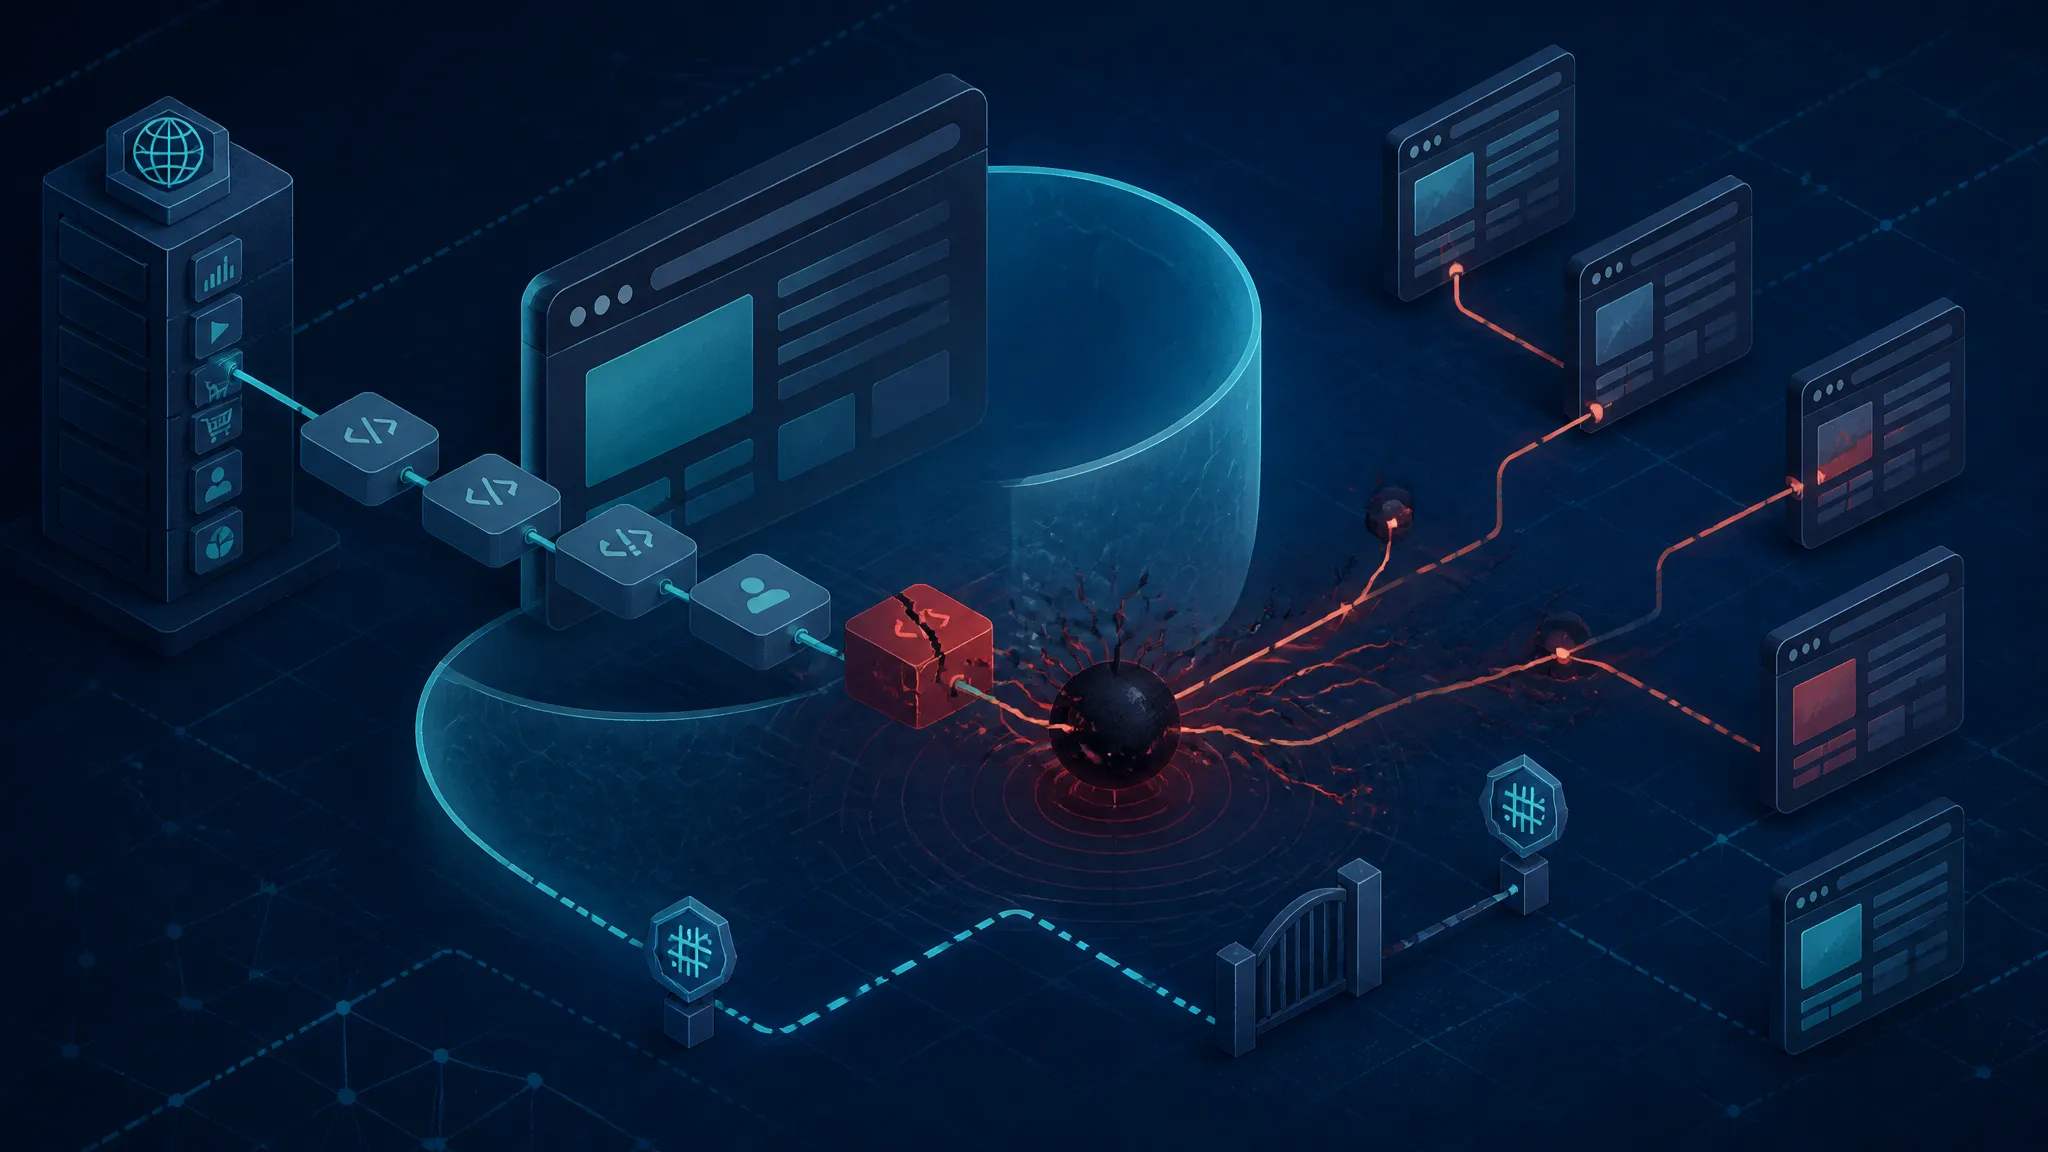
A deep technical walkthrough for auditing third-party script loads and injected tags after the Optimizely breach, covering blast-radius tracing, CSP/SRI controls, script allowlisting, monitoring, and rapid isolation of malicious vendor code.
supply-chain-securitythird-party-scriptscontent-security-policy