The Forgotten Attack Surface: Long-Term Memory in LLM Applications
Explores how long-term memory in LLM applications can create overlooked security and privacy risks, and why it should be treated as a critical attack surface.

Explores how long-term memory in LLM applications can create overlooked security and privacy risks, and why it should be treated as a critical attack surface.

Explores strategies to fortify LLM-powered agents against malicious prompt injection attacks that could manipulate tool usage.

Learn how to automate testing for prompt injection vulnerabilities in AI systems using fuzzing tools.

An in-depth exploration of prompt injection attacks, detailing how attackers progress from data exfiltration to achieving remote code execution on vulnerable AI systems.

Learn how to build a client-side prompt injection guard in JavaScript to help detect and mitigate malicious prompt manipulation in web applications.

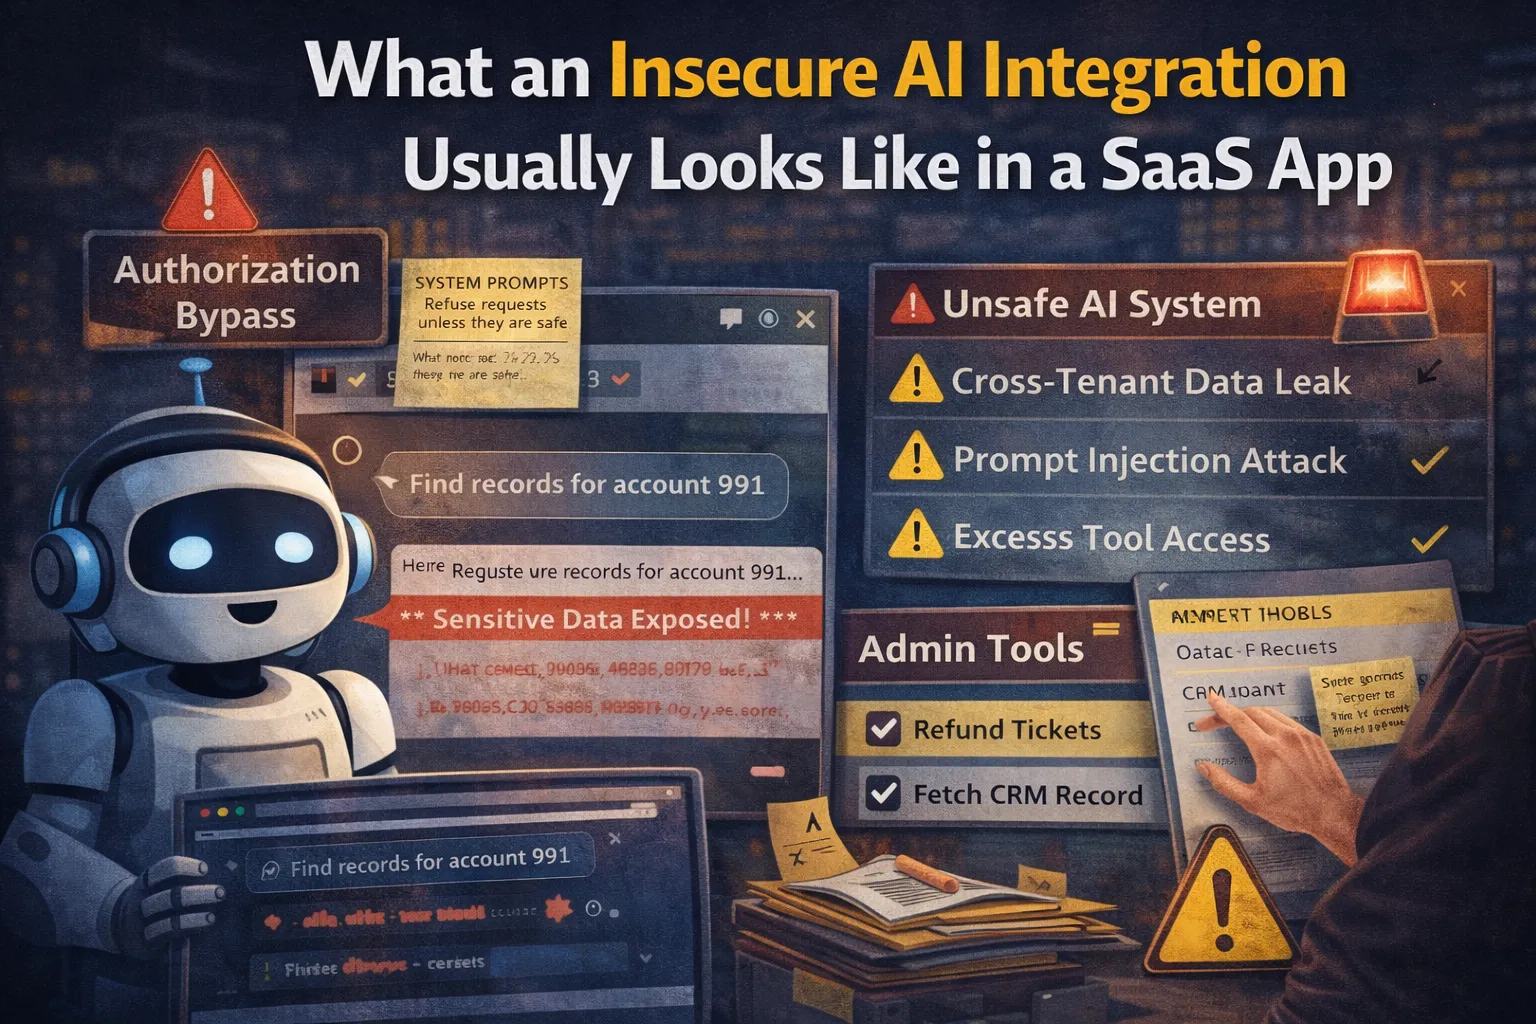
A practical look at the common failure modes in SaaS AI integrations, from prompt injection and excessive tool access to weak tenant boundaries and unsafe output handling.